
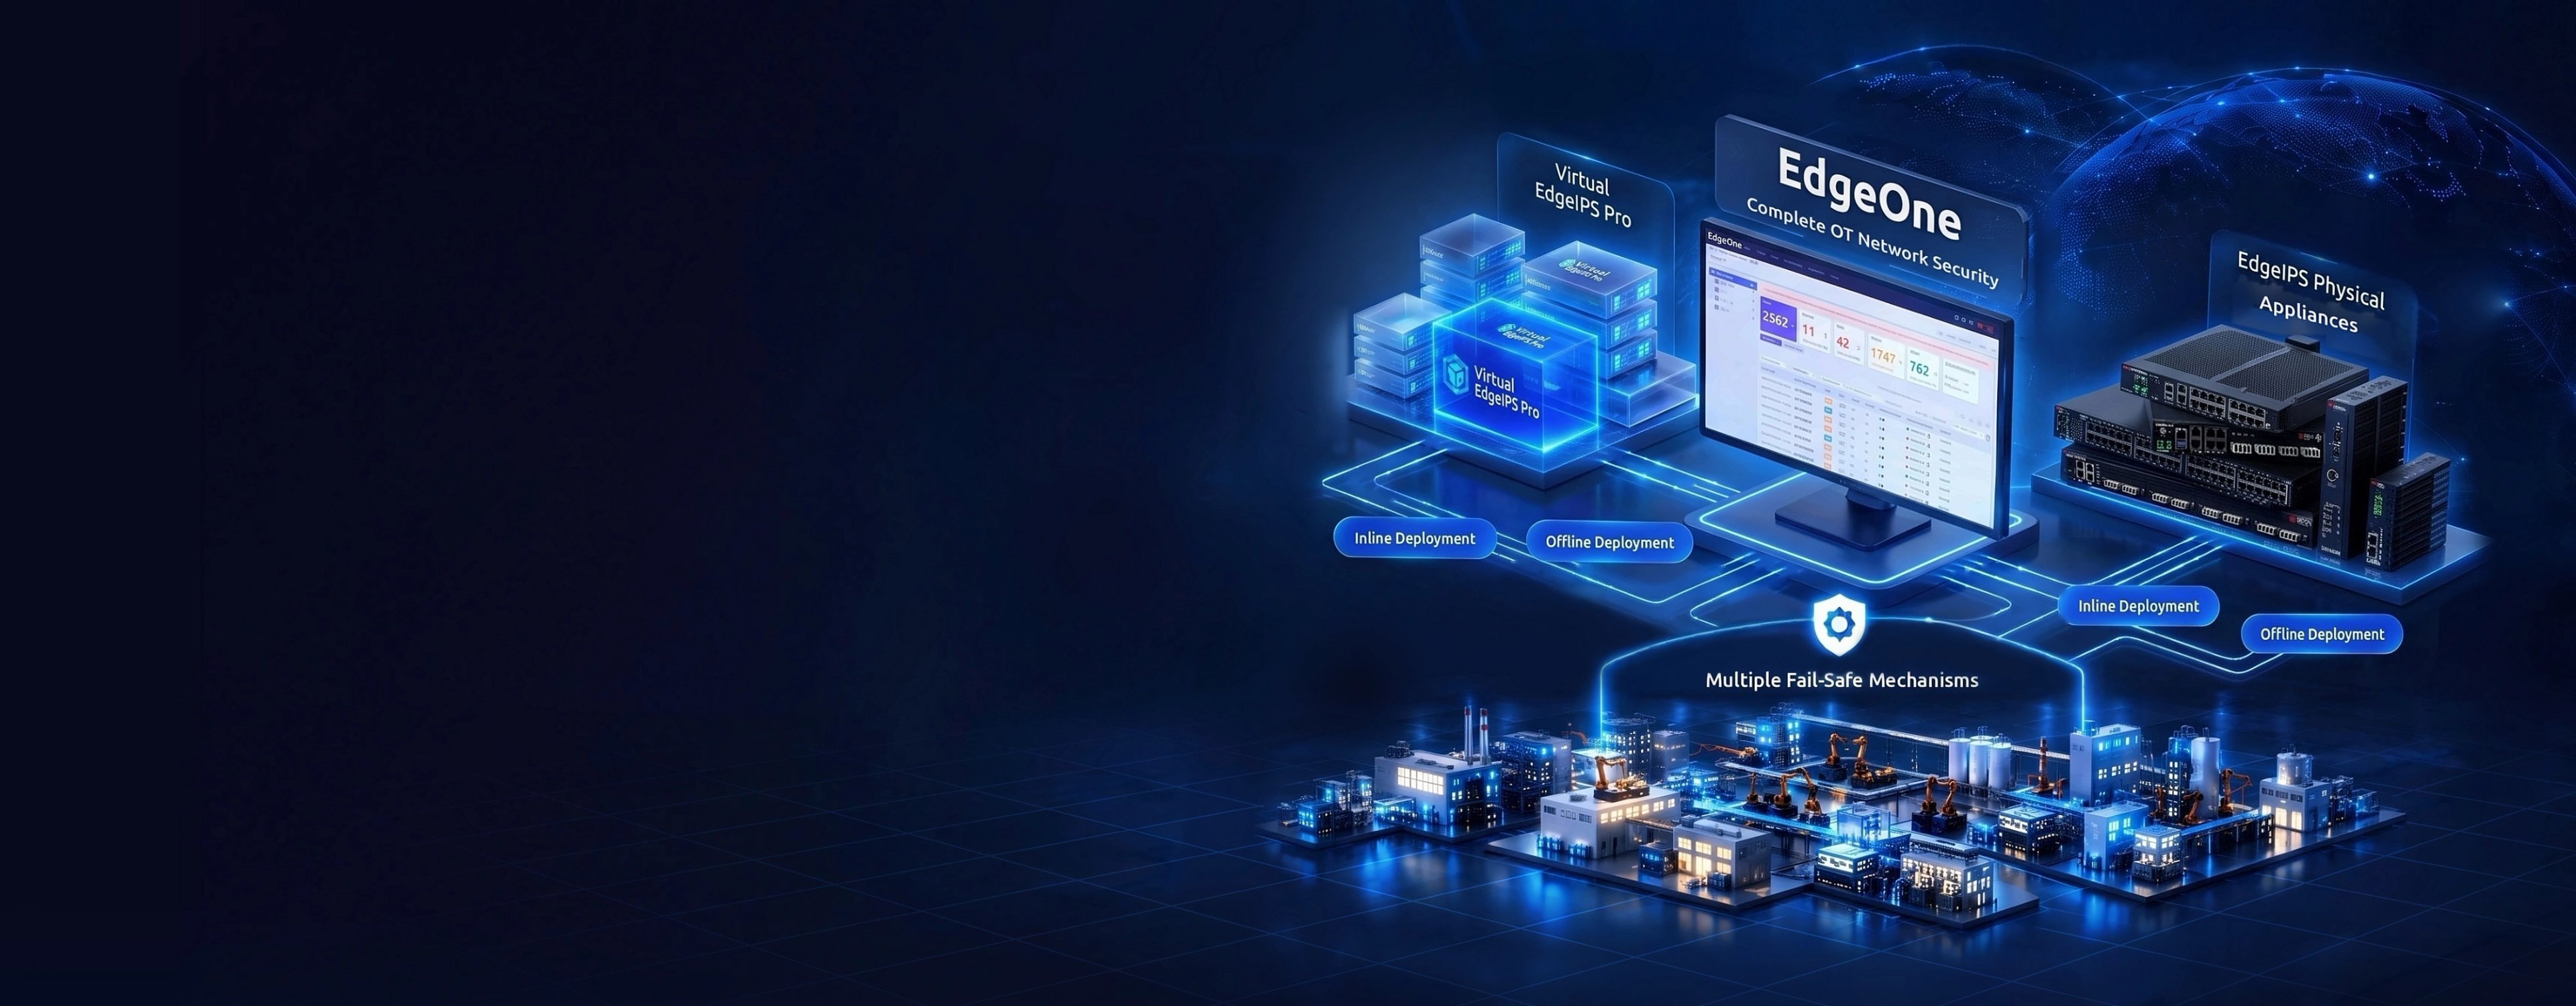
See Every Asset. Manage Every Policy. One Console.
Now EdgeOne answers back. Ask it a question in plain language, asset status, policy coverage, today's highest-severity alert, and get an answer scoped to what it already protects.
Centralized management console unifying policy control, asset visibility, and vulnerability detection across all EdgeIPS and EdgeFire deployments, on hardware or in your virtualized infrastructure. An AI-enhanced alert engine turns every detection into an answer, and a built-in MCP connector lets your own AI agents ask for that answer directly. On-premises or cloud.
EdgeOne manages your Edge deployment with centralized policy control and network-based vulnerability detection for OT environments.
Managing distributed network security should not mean logging into separate consoles for every device or missing vulnerabilities in systems that cannot run agents. EdgeOne unifies fragmented Edge deployments into one ecosystem. Asset Vulnerability Management (AVM) identifies CVEs through network traffic analysis alone, covering systems that cannot accept scanning. Deploy on-premises or in the cloud, and manage hardware and virtual Edge appliances from the same console. Either way, you get centralized policy management and security orchestration for every Edge device.
Your Edge Deployment, Unified
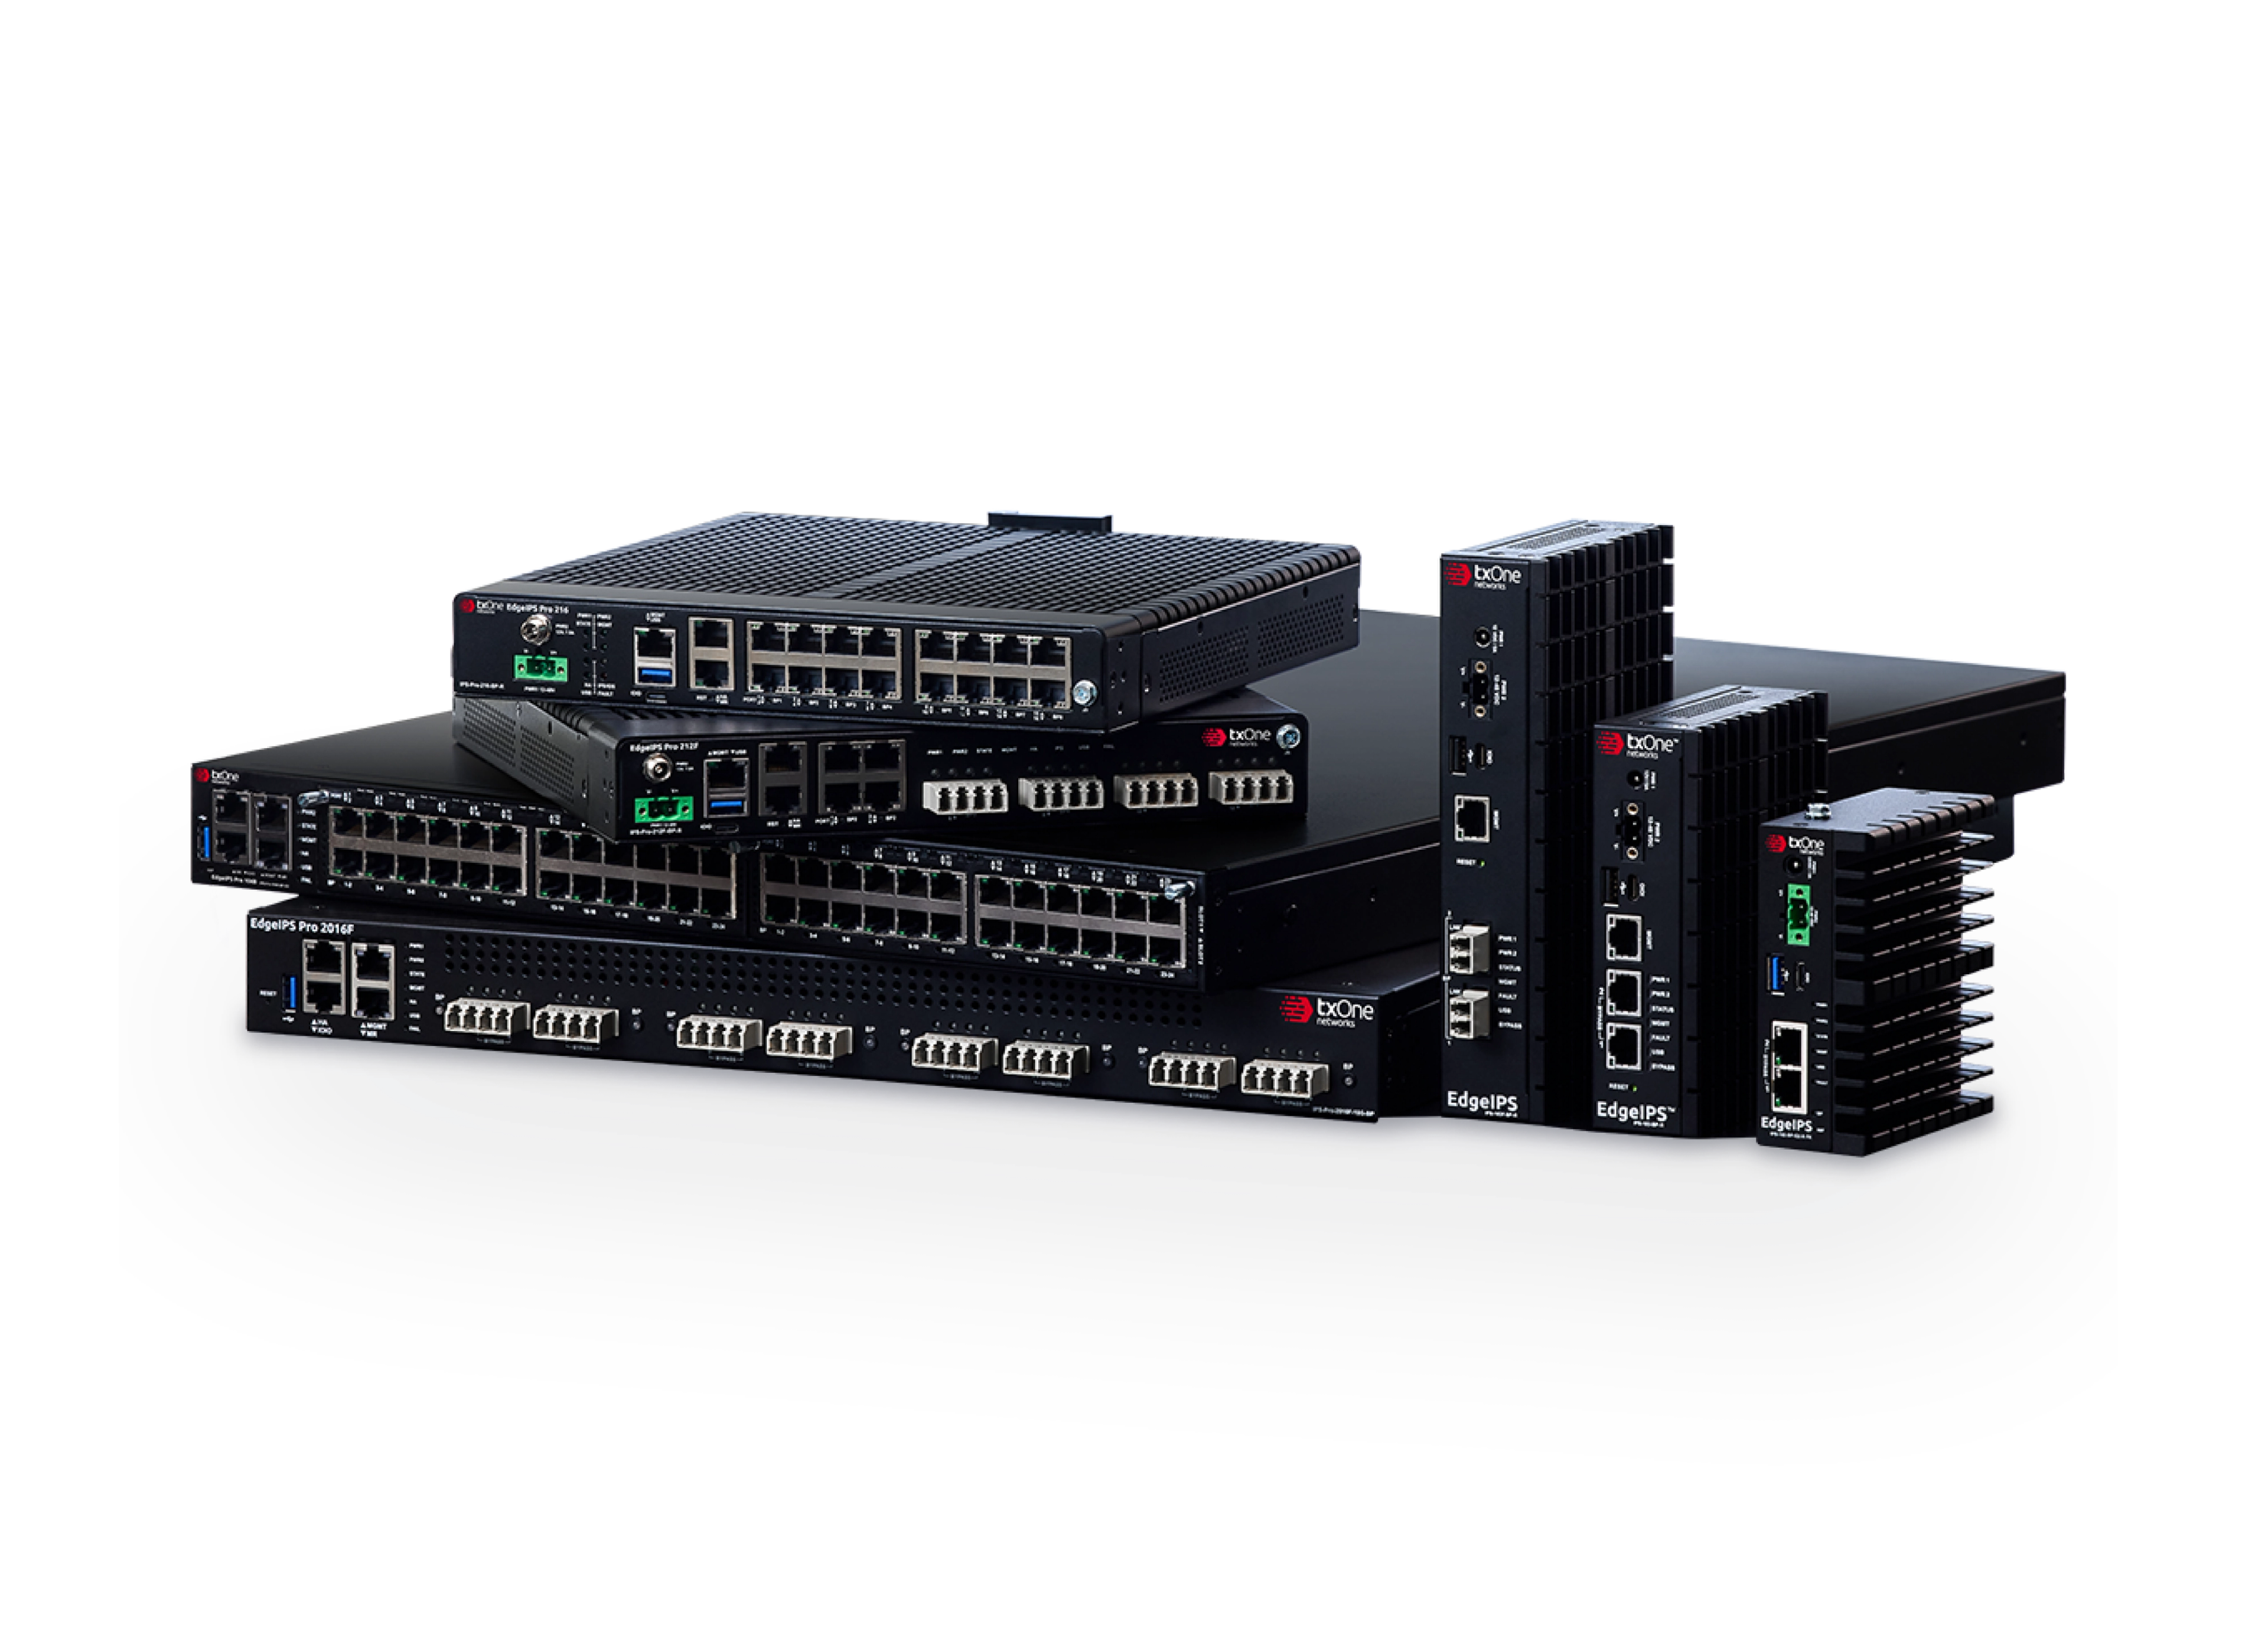
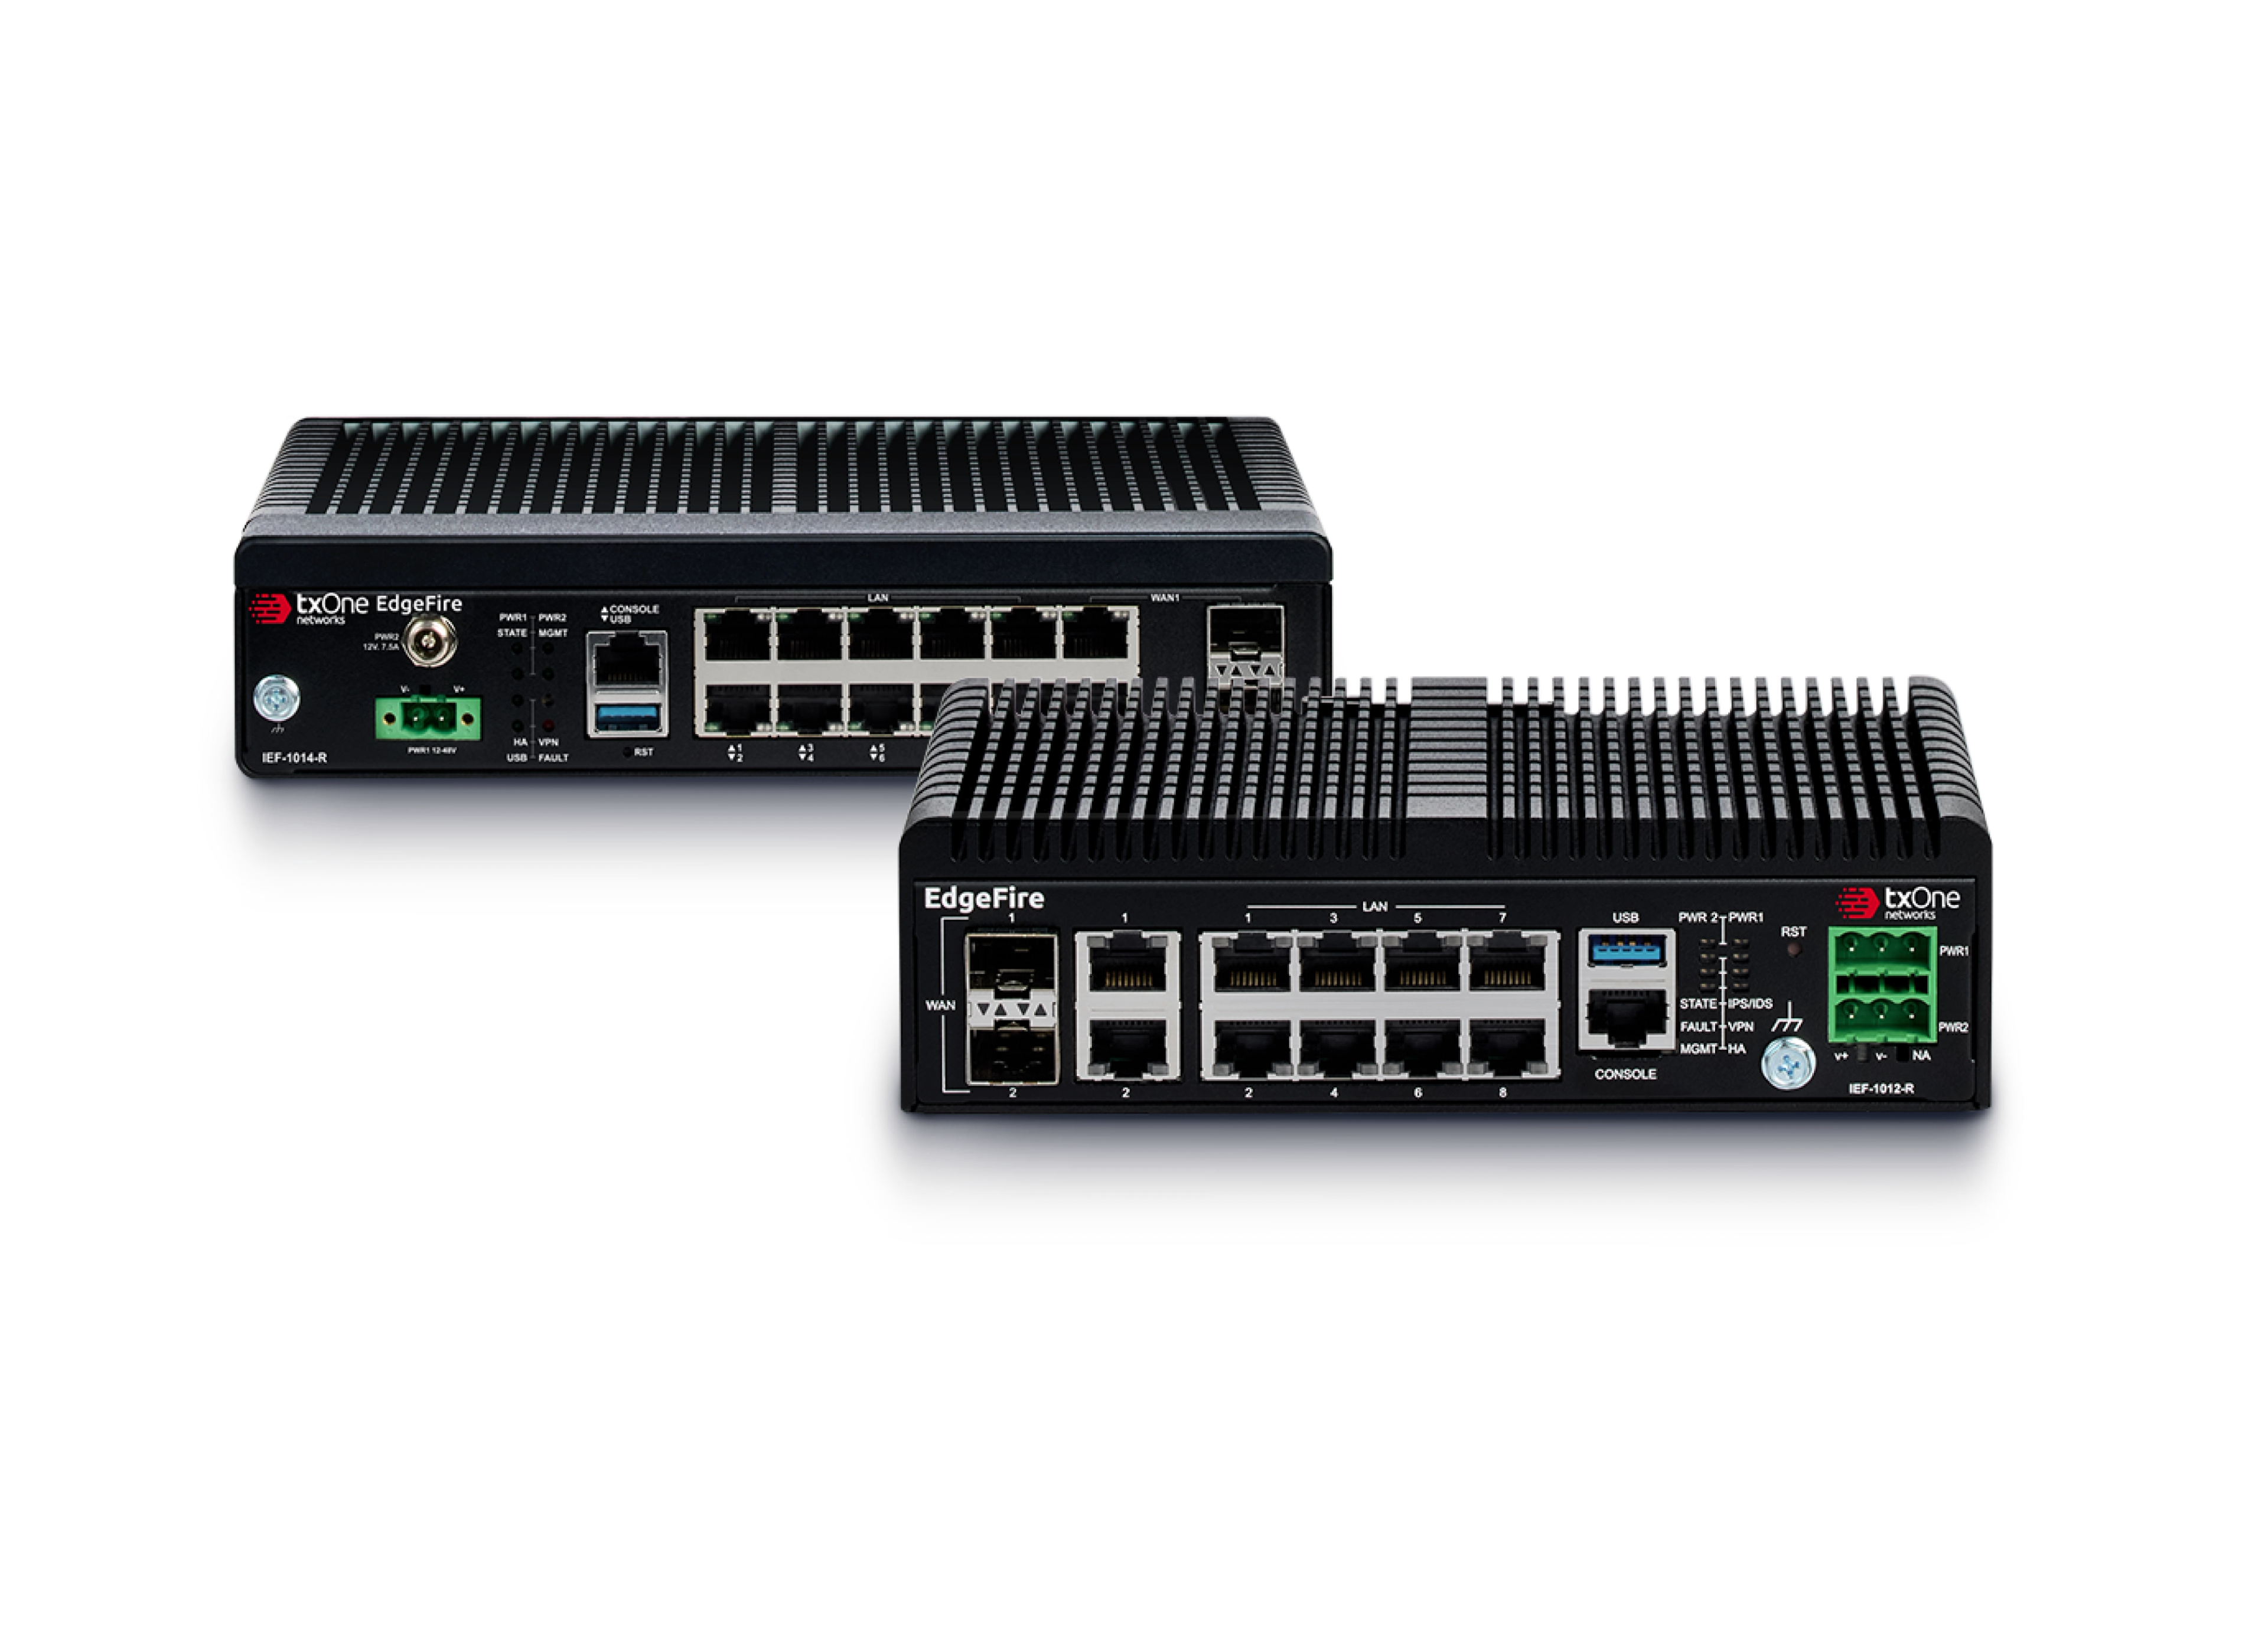
Every EdgeIPS and EdgeFire device you deploy, physical or virtual, closes a security gap, but it also opens a management gap. At 50+ devices across multiple sites, you lose the ability to see your security posture, enforce consistent policies, or respond to threats at enterprise scale. EdgeOne closes that gap, and now does more of the work itself: one console for every Edge device, every policy, every alert, with an AI engine that clusters the alerts and a connector that answers questions about all of it in plain language.
AI-Ready Operations
A built-in MCP connector lets authorized AI agents query and act on fleet, policy, and alert data in plain language, inside EdgeOne's own security perimeter.
Single Pane of Glass
Manage all EdgeIPS and EdgeFire devices, hardware and virtual, from one unified console.
OT Asset Visibility
Automatic discovery and inventory of all OT assets across the network.
Coordinated Response
Threat intelligence sharing and synchronized policy updates across all devices.
OT Security Challenges
Critical challenges that EdgeOne is purpose-built to solve
01 / 03
Device-by-Device Management
Every EdgeFire and EdgeIPS device deployed, physical or virtual, requires individual configuration, updates, and monitoring. At scale, device-by-device management becomes unmanageable and error-prone.
Device-by-Device Management
Every EdgeFire and EdgeIPS device deployed, physical or virtual, requires individual configuration, updates, and monitoring. At scale, device-by-device management becomes unmanageable and error-prone.
Key Features
Discover how EdgeOne protects your OT environment
01 / 07
AI-Enhanced Alert Engine
An AI engine clusters every event by real-world severity and builds the attack chain automatically: detect, analyze, match CVE, recommend, so your team spends seconds, not hours, deciding what matters. Customizable widgets keep alerts, assets, CVEs, and incidents visible at a glance.
Key Capabilities
Real-World Applications
See how organizations deploy EdgeOne in production environments
01 / 06
Single Factory Management
On-premises EdgeOne deployment for manufacturing plants with 200 to 1,000 Edge devices.
Single Factory Management
On-premises EdgeOne deployment for manufacturing plants with 200 to 1,000 Edge devices.
Deployment Options
Choose the right deployment model for EdgeOne
On-Premises Virtual Appliance
Deploy EdgeOne as a virtual machine in your existing data center infrastructure for complete control over your security management platform.
Cloud and Hybrid Deployment
Deploy EdgeOne on AWS, Azure, or a hybrid architecture for multi-site organizations. Central management with regional data residency options. Not available for air-gapped environments.
Technology
Technologies powering EdgeOne
Centralized Policy Management
Scalable Security Orchestration
EdgeOne enables centralized creation, testing, and deployment of security policies across thousands of EdgeIPS and EdgeFire devices. Template-based policy management reduces configuration time while ensuring consistency.
- Template-based policy creation
- Staged rollout with validation
- Role-based access control
- Audit logging for compliance
Manage thousands of OT security devices from a single console.
Deploy EdgeOne in 4 Steps
A streamlined implementation process designed for OT environments with zero disruption to operations.
Week 1: Deploy EdgeOne virtual appliance (on-premises or cloud)
Week 2: Connect existing Edge devices for unified management
Month 1: Configure AVM and policy management workflows
Ongoing: Expand with Sennin for complete TXOne orchestration
Operational & Protected
Technical Specifications
Seamless Integration with EdgeOne
Designed to integrate into existing OT infrastructure without disrupting operations.
What Our Customers Say
“Within this context, TXOne Networks emerged as the ideal technology partner, capable of responding precisely to Ansaldo Energia’s requirements.”
“Thanks to OT security solution Stellar, TXOne Networks helps us mitigate risks that we couldn't address yesterday without making significant financial investments.”
Related Resources
Explore resources related to EdgeOne
EdgeOne Datasheet
EdgeOne is the holistic industrial central management console that unifies visibility, vulnerability detection, and policy control across your entire Edge network security deployment. Manage up to 1,000 nodes from a single console, available on-premises or in the cloud.
See All Resources
Browse all resources related to edgeone
Related Products
Ready for Unified Network Security Visibility?
See how EdgeOne consolidates management of your Edge deployment with network-based vulnerability detection. Request a demo.