

Inline Protection Without the Production Risk
Transparent intrusion prevention with under half a millisecond of delay. Deploy inline to block threats, or offline on a SPAN port to watch first. No IP changes or network redesign. Fail-safe bypass ensures network continuity.
End the Standoff Between Security and Operations
Your security team wants inline protection. Your operations team wants zero production risk. EdgeIPS delivers both, and now does more of the work itself: an AI engine builds and tunes security policy automatically, and the same protection architecture runs on physical appliances or the new vEdgeIPS Pro virtual appliance.
AI-Powered Policy Generation
An AI engine builds, aggregates, and tunes your policy automatically, cutting deployment effort by more than 90%.
Physical or Virtual
vEdgeIPS Pro brings the same inline, fail-safe protection to virtualized OT infrastructure, with no IP reconfiguration or network topology redesign required.
Four AI Pillars, One Closed Loop
AI-powered Asset Intelligence, Policy Automation, Threat Alert Visibility, and OT Integration.
Per-Segment Hardware Bypass
Gen3 hardware bypass on every port pair ensures production continuity during any event.
Hybrid Protocol Filtering
Granular OT protocol inspection without firmware upgrades, new protocols added dynamically.
Inline Asset Protection
Compact 1-to-1 IPS appliances for individual critical assets

EdgeIPS 102 Gen2
DIN-Rail MountCompact protection for a single critical device.

EdgeIPS 103
DIN-Rail MountFast, compact protection for a single critical device.

EdgeIPS 103F
DIN-Rail MountFiber connections for a single critical link.

EdgeIPS LE 102
DIN-Rail MountCompact next-gen IPS for cost-sensitive environments
Multi-Segment Protection
Multi-port appliances protecting multiple network segments from a single device

EdgeIPS Pro 212F
DIN-Rail MountMulti-segment protection for copper and fiber links.

EdgeIPS Pro 216
DIN-Rail MountEight-segment protection in two versions: Commercial for temperature-controlled sites, or Rugged for harsh environments.
Production & Data Center Scale
High-performance rack-mounted appliances for large-scale OT network protection

EdgeIPS Pro 732
1U RackmountHigh-capacity protection for large production sites.

EdgeIPS Pro 1048 Gen2
1U RackmountModular 48-port IPS for large-scale network segmentation

EdgeIPS Pro 2096 Gen2
2U RackmountMaximum port density for the largest networks.

EdgeIPS Pro 4016F
1U RackmountThe fastest EdgeIPS, built for high-speed fiber networks.

EdgeIPS Pro 2016F
1U RackmountHigh-speed fiber protection for demanding networks.
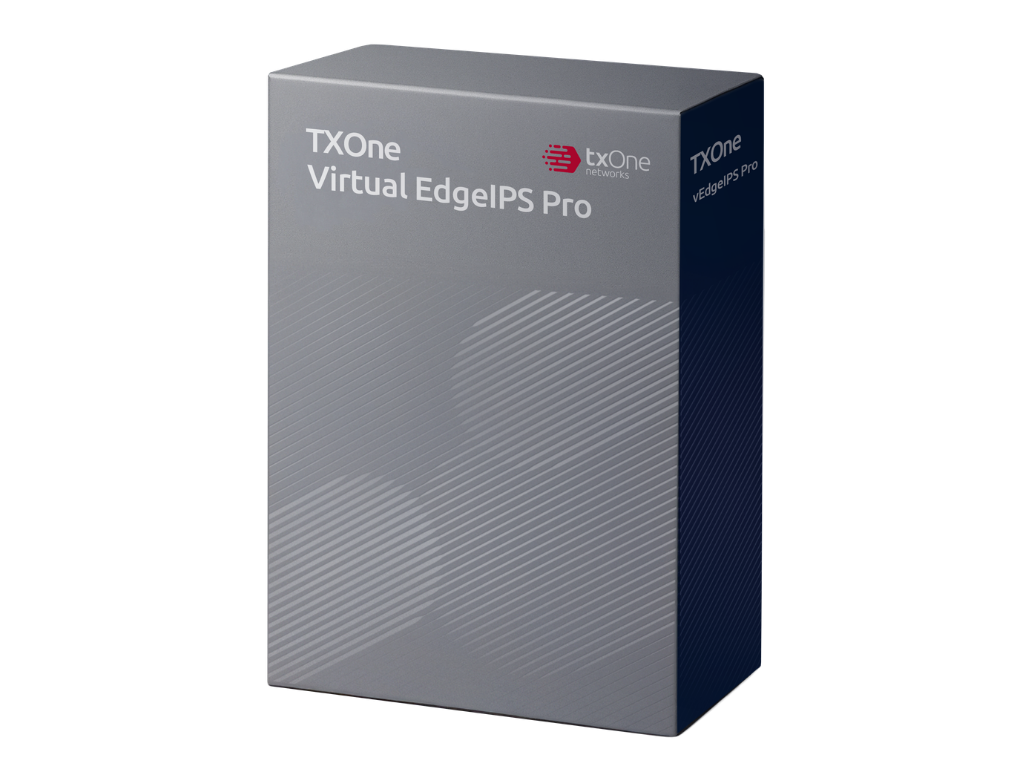
vEdgeIPS Pro
Virtual ApplianceThe same OT protection, delivered as a virtual appliance.
OT Security Challenges
Critical challenges that EdgeIPS Family is purpose-built to solve
01 / 04
Network Redesign Required
IT security appliances require IP address changes and network architecture modifications.
Network Redesign Required
IT security appliances require IP address changes and network architecture modifications.
Key Features
Discover how EdgeIPS Family protects your OT environment
01 / 07
AI-Powered Policy Generation
An AI engine watches traffic per asset, builds a baseline allowlist, then aggregates and tunes the rule set automatically, compressing policy deployment from weeks to hours and cutting manual rule-writing by more than 90%.
Key Capabilities
AI-Powered Policy Generation
An AI engine watches traffic per asset, builds a baseline allowlist, then aggregates and tunes the rule set automatically, compressing policy deployment from weeks to hours and cutting manual rule-writing by more than 90%.
Key Capabilities
Real-World Applications
See how organizations deploy EdgeIPS Family in production environments
01 / 07
Critical Legacy Asset Protection
EdgeIPS 102 Gen2, 103, or LE 102 - One unit in front of a single asset you cannot patch, replace, or take offline, such as a production tool worth millions that the line depends on. One-to-one inline protection at a fraction of the cost of an outage.
Critical Legacy Asset Protection
EdgeIPS 102 Gen2, 103, or LE 102 - One unit in front of a single asset you cannot patch, replace, or take offline, such as a production tool worth millions that the line depends on. One-to-one inline protection at a fraction of the cost of an outage.

For Operations Teams
Deploy inline network security, on hardware or virtualized infrastructure, without touching a single IP address. An AI engine builds the security policy for you, and bypass technology provides production continuity assurance, even during maintenance or failures.
For Operations Teams
Deploy inline network security, on hardware or virtualized infrastructure, without touching a single IP address. An AI engine builds the security policy for you, and bypass technology provides production continuity assurance, even during maintenance or failures.
- Zero network changes required
- AI-generated policy in hours, not weeks
- Bypass on every segment, physical or virtual
- Physical or virtual appliances
Technology
Technologies powering EdgeIPS Family
CPSDR Networking Technology
Predictive Threat Detection for Industrial Networks
EdgeIPS uses CPSDR to identify and predict anomalous network behaviors at the earliest stages. Combined with deep OT protocol understanding, it provides proactive defense against sophisticated threats targeting industrial control systems.
- Predictive anomaly detection across network segments
- Proactive threat blocking before production impact
- Asset-aware behavioral analysis
- Continuous network posture assessment
Designed for inline deployment without production disruption
The Impossible Choice: Protection vs. Production
Your security team knows inline protection is the standard. Your operations team knows any inline device can become a single point of failure. A single false positive or device failure could halt production lines worth millions per hour.
Deployment Method
Requires IP address changes and network architecture modifications, causing months of downtime and risk
Transparent deployment with no IP changes; production runs throughout installation
Failover Protection
No hardware bypass; device failure stops production
Gen3 hardware bypass on all segments with sub-microsecond switchover
Protocol Support
Cannot inspect Modbus, SECS/GEM, or S7Comm; industrial attacks are invisible
Deep inspection for 180+ industrial protocols with CPSDR predictive detection
EdgeIPS Pro eliminates the impossible choice. Your security team gets inline prevention. Your operations team gets the hardware bypass guarantee.
Deploy EdgeIPS Family in 4 Steps
A streamlined implementation process designed for OT environments with zero disruption to operations.
Week 1: Technical assessment identifying deployment priorities
Week 2-3: Pilot deployment with transparent installation on hardware or virtual appliances
Month 1-2: Expand coverage with AI-powered policy generation
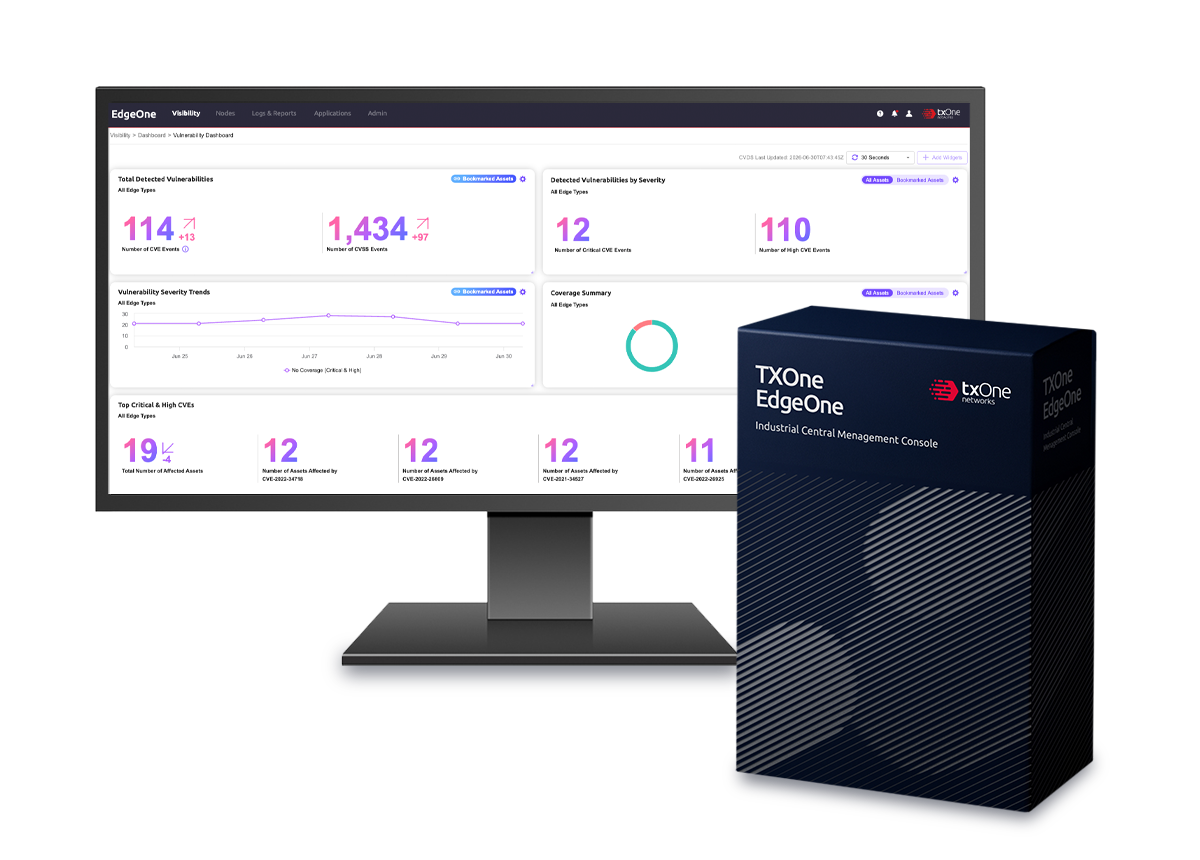
Ongoing: EdgeOne integration for centralized visibility
Operational & Protected
Technical Specifications
Seamless Integration with EdgeIPS Family
Designed to integrate into existing OT infrastructure without disrupting operations.
What Our Customers Say
“Within this context, TXOne Networks emerged as the ideal technology partner, capable of responding precisely to Ansaldo Energia’s requirements.”
“Thanks to OT security solution Stellar, TXOne Networks helps us mitigate risks that we couldn't address yesterday without making significant financial investments.”
Related Resources
Explore resources related to EdgeIPS Family
EdgeIPS Pro 212F Datasheet
EdgeIPS Pro 212F delivers 1.8 Gbps+ threat prevention throughput with 6 Gen3 hardware bypass segments. Compact rugged form factor with copper and fiber interfaces for production cell and control system network protection.
EdgeIPS Pro 2016F/4016F Datasheet
EdgeIPS Pro 2016F and 4016F are rack-mounted intrusion prevention systems purpose-built for large industrial facilities running fiber infrastructure, delivering 20 to 40 Gbps threat prevention throughput without becoming a bottleneck in the network they protect.
EdgeIPS Pro 1048/2096 Datasheet
EdgeIPS Pro 1048 and 2096 deliver enterprise-scale OT network protection — the 1048 supports up to 24 hardware segments and 10 Gbps IMIX throughput, while the 2096 doubles that with up to 48 segments and 20 Gbps throughput. Modular architecture with up to 96 copper or fiber ports for large manufacturing complexes.
See All Resources
Browse all resources related to edgeips
Ready for Inline Protection Without Production Risk?
See bypass technology and transparent deployment in action, on hardware or virtual appliances. Request a technical assessment for your network environment.