
Network Security That Speaks Your Proprietary Protocols
Your IT firewalls filter by port and protocol. Attackers exploit the industrial commands hiding inside. TXOne Edge blocks at the OT command level.
Inline threat prevention across 180+ industrial protocols, both standard and proprietary, with sub-second blocking, 1,500+ OT-native signatures, and an AI engine that finds your assets, writes your policy, and prioritizes your alerts. Protection that deploys in 60 minutes with zero network changes, on hardware or virtual infrastructure.
Industrial Network Security Challenges
Industrial networks face security challenges that traditional IT solutions cannot address without compromising the operations they are meant to protect.
01 / 05
IT Firewalls Cannot See Industrial Traffic
Enterprise firewalls treat Modbus, EtherNet/IP, CIP, and SECS/GEM as generic packets and cannot distinguish legitimate PLC commands from malicious payloads, leaving attack vectors invisible.
IT Firewalls Cannot See Industrial Traffic
Enterprise firewalls treat Modbus, EtherNet/IP, CIP, and SECS/GEM as generic packets and cannot distinguish legitimate PLC commands from malicious payloads, leaving attack vectors invisible.
Network Security Framework
Comprehensive OT network protection architecture.
01 / 04
Network Segmentation
Micro-segmentation for critical OT assets without network redesign
Key Capabilities
Network Segmentation
Micro-segmentation for critical OT assets without network redesign
Key Capabilities
Industrial Network Protection
TXOne Edge provides inline network security purpose-built for operational technology, protecting your industrial protocols with zero operational compromise.
01 / 07
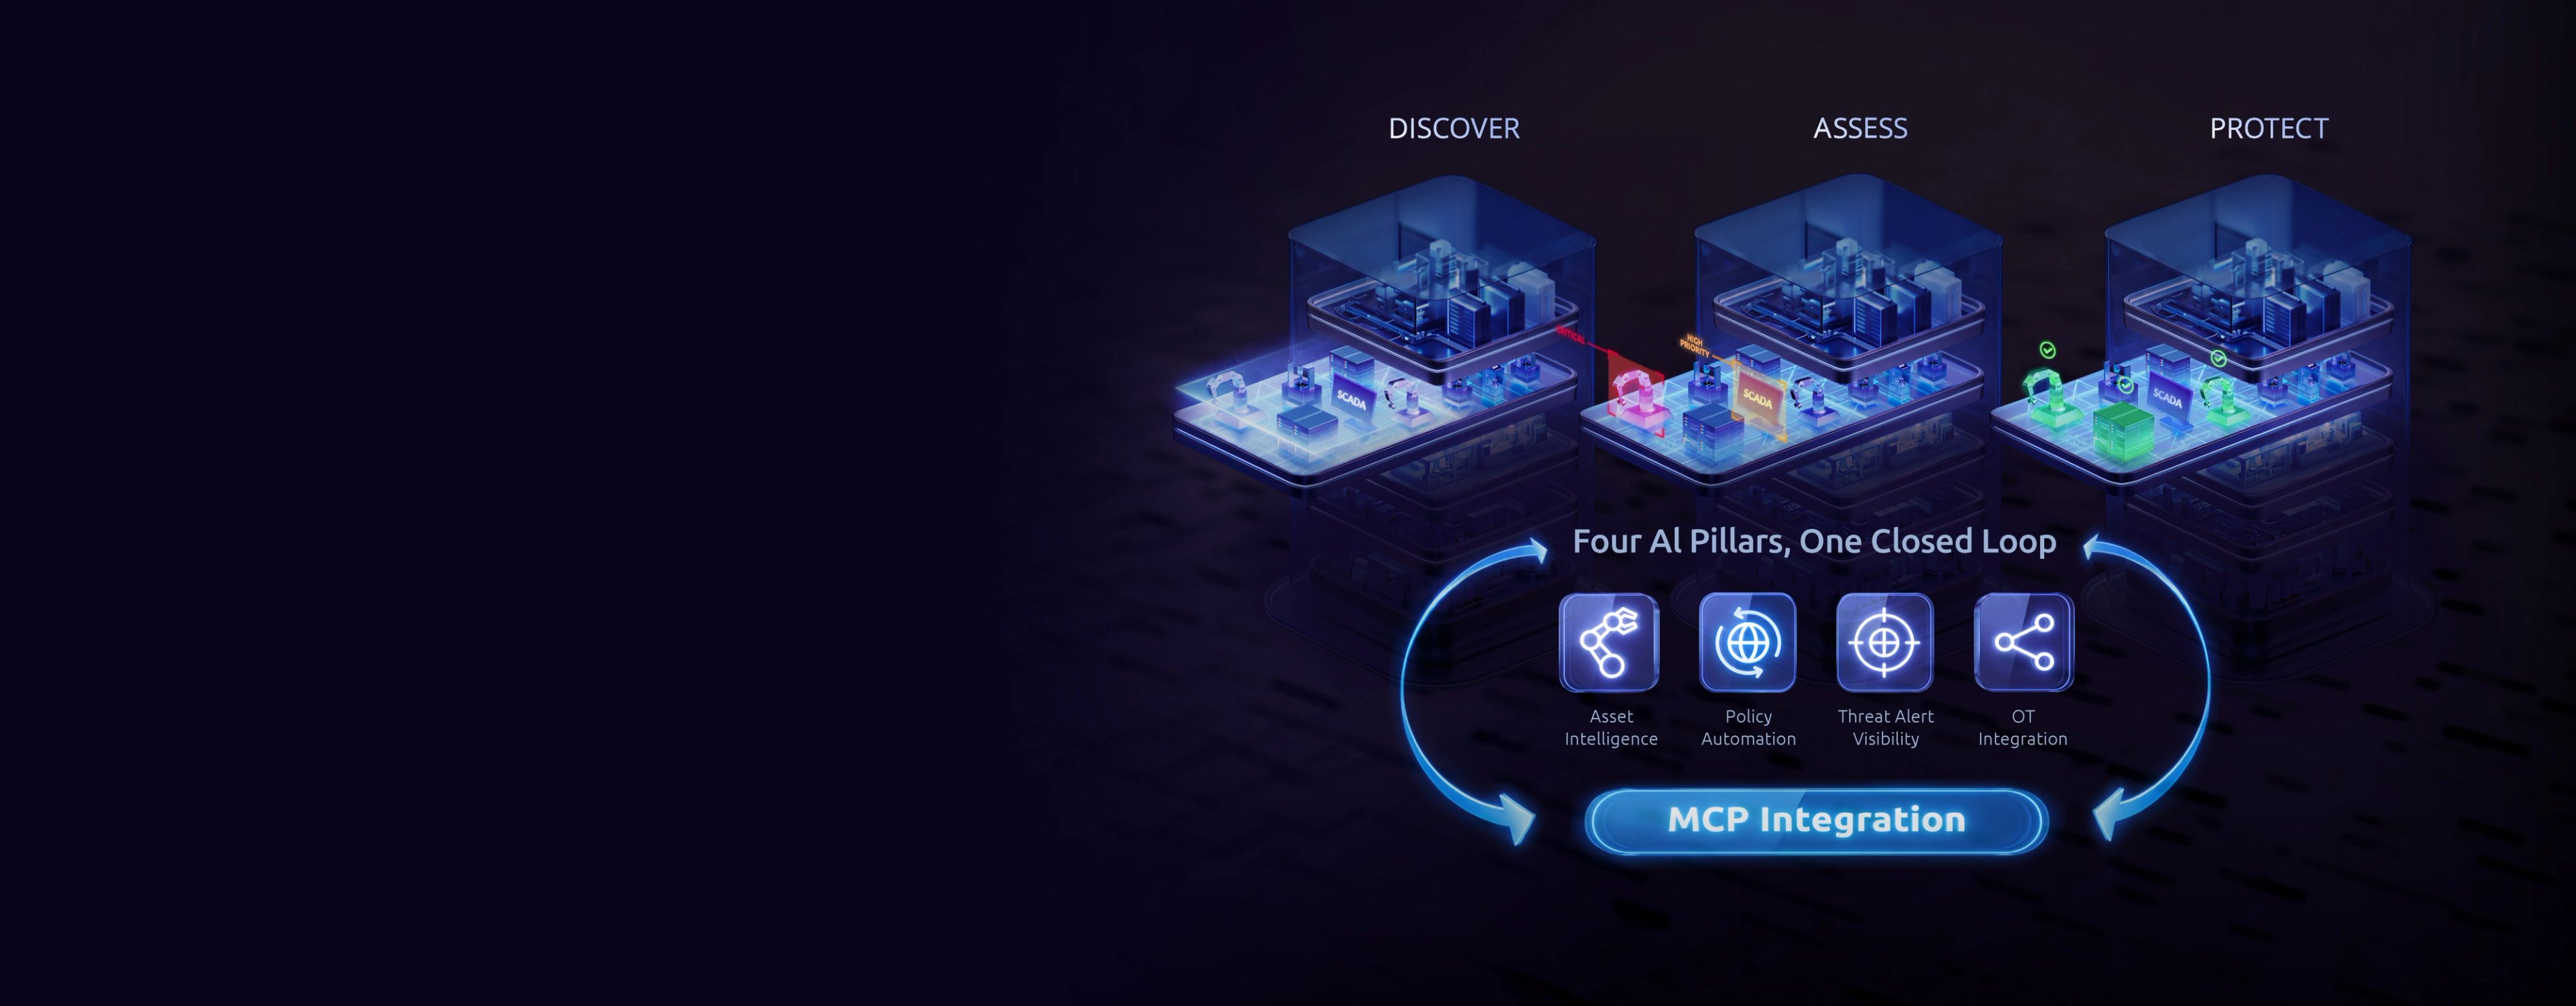
AI-Powered at Every Stage
A closed AI loop now runs through Discover, Assess, and Protect: it fingerprints legacy and unmanaged assets that signature-only tools miss and maps them to known vulnerabilities, clusters and prioritizes every alert into one next step, and writes and tunes its own policy in hours instead of weeks. All of it is reachable through a built-in MCP connector, so your own AI tools can ask for a status update in plain language instead of you pulling one together by hand.
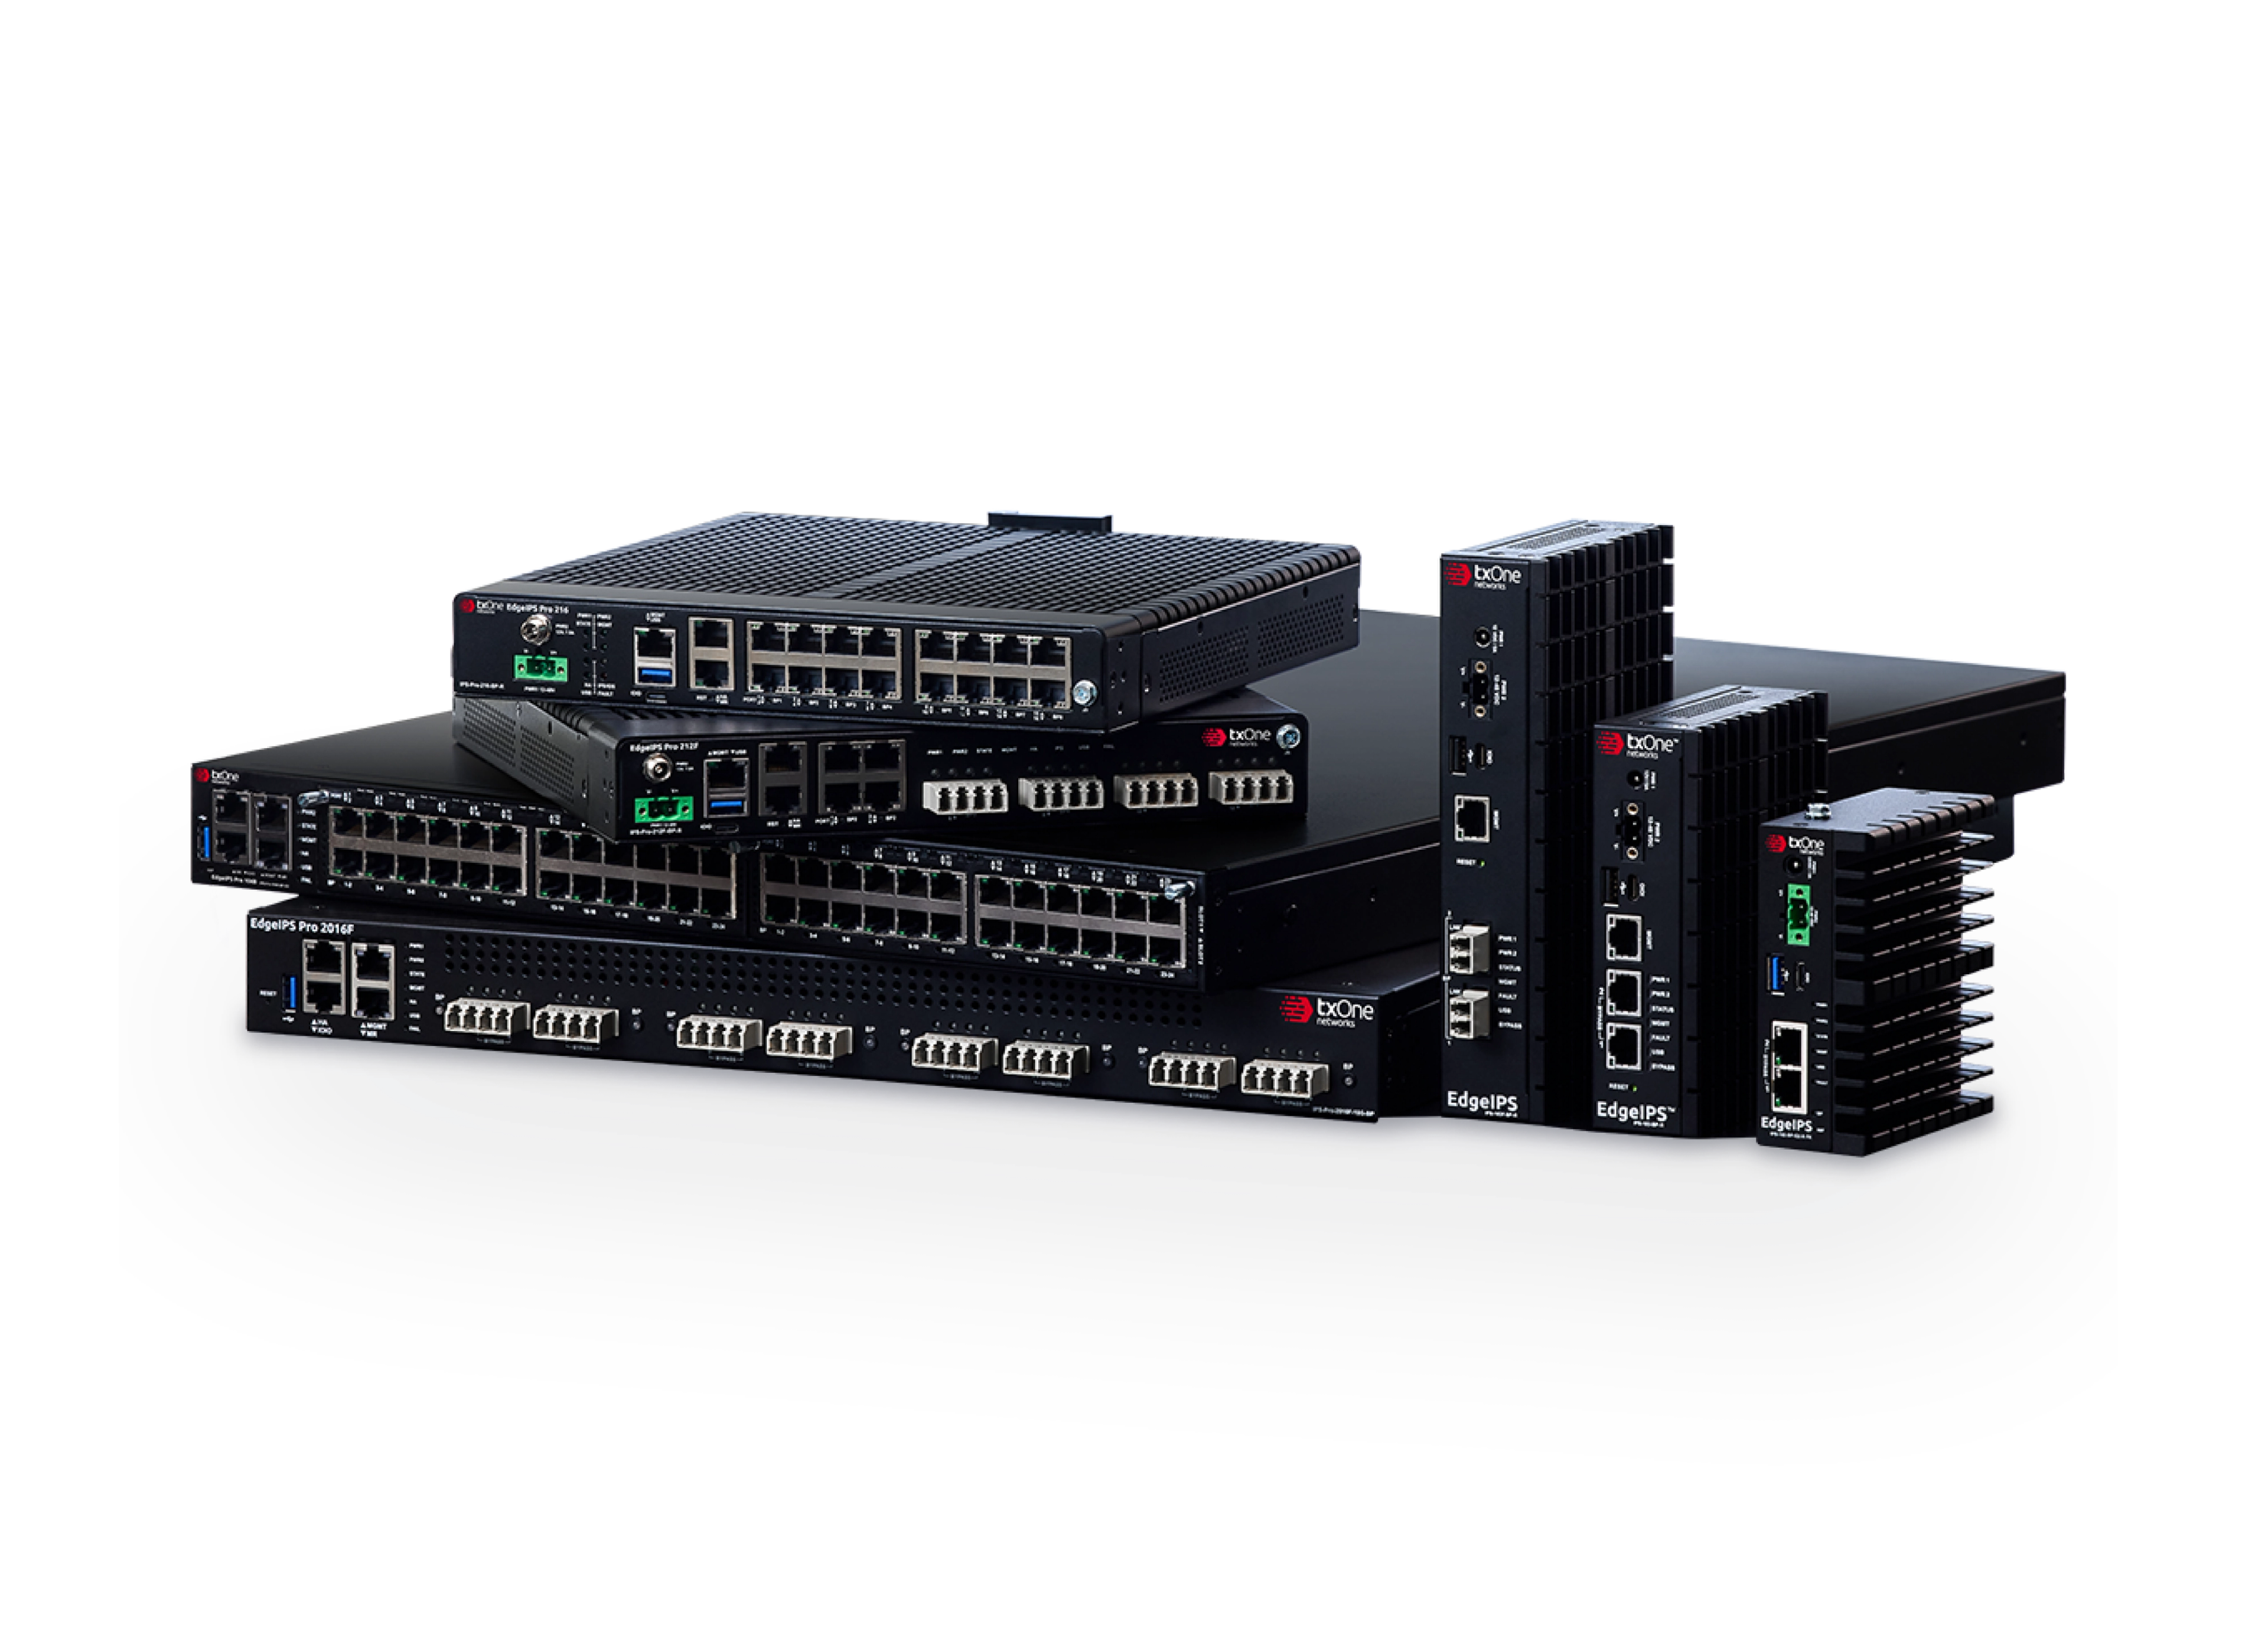
EdgeIPS Family
Intent-Based Industrial IPS
Scalable OT network security with predictive detection and intelligent policy automation
OT network security with AI-driven, asset-centric auto rule learning and policy generation, plus CPSDR predictive security across 180+ industrial protocols. Fail-safe bypass keeps your network running if a device fails. Choose from single-segment units, multi-segment models, rack-mount systems, or a virtual appliance. The family scales to 48 segments in one device and up to 40 Gbps threat prevention throughput.
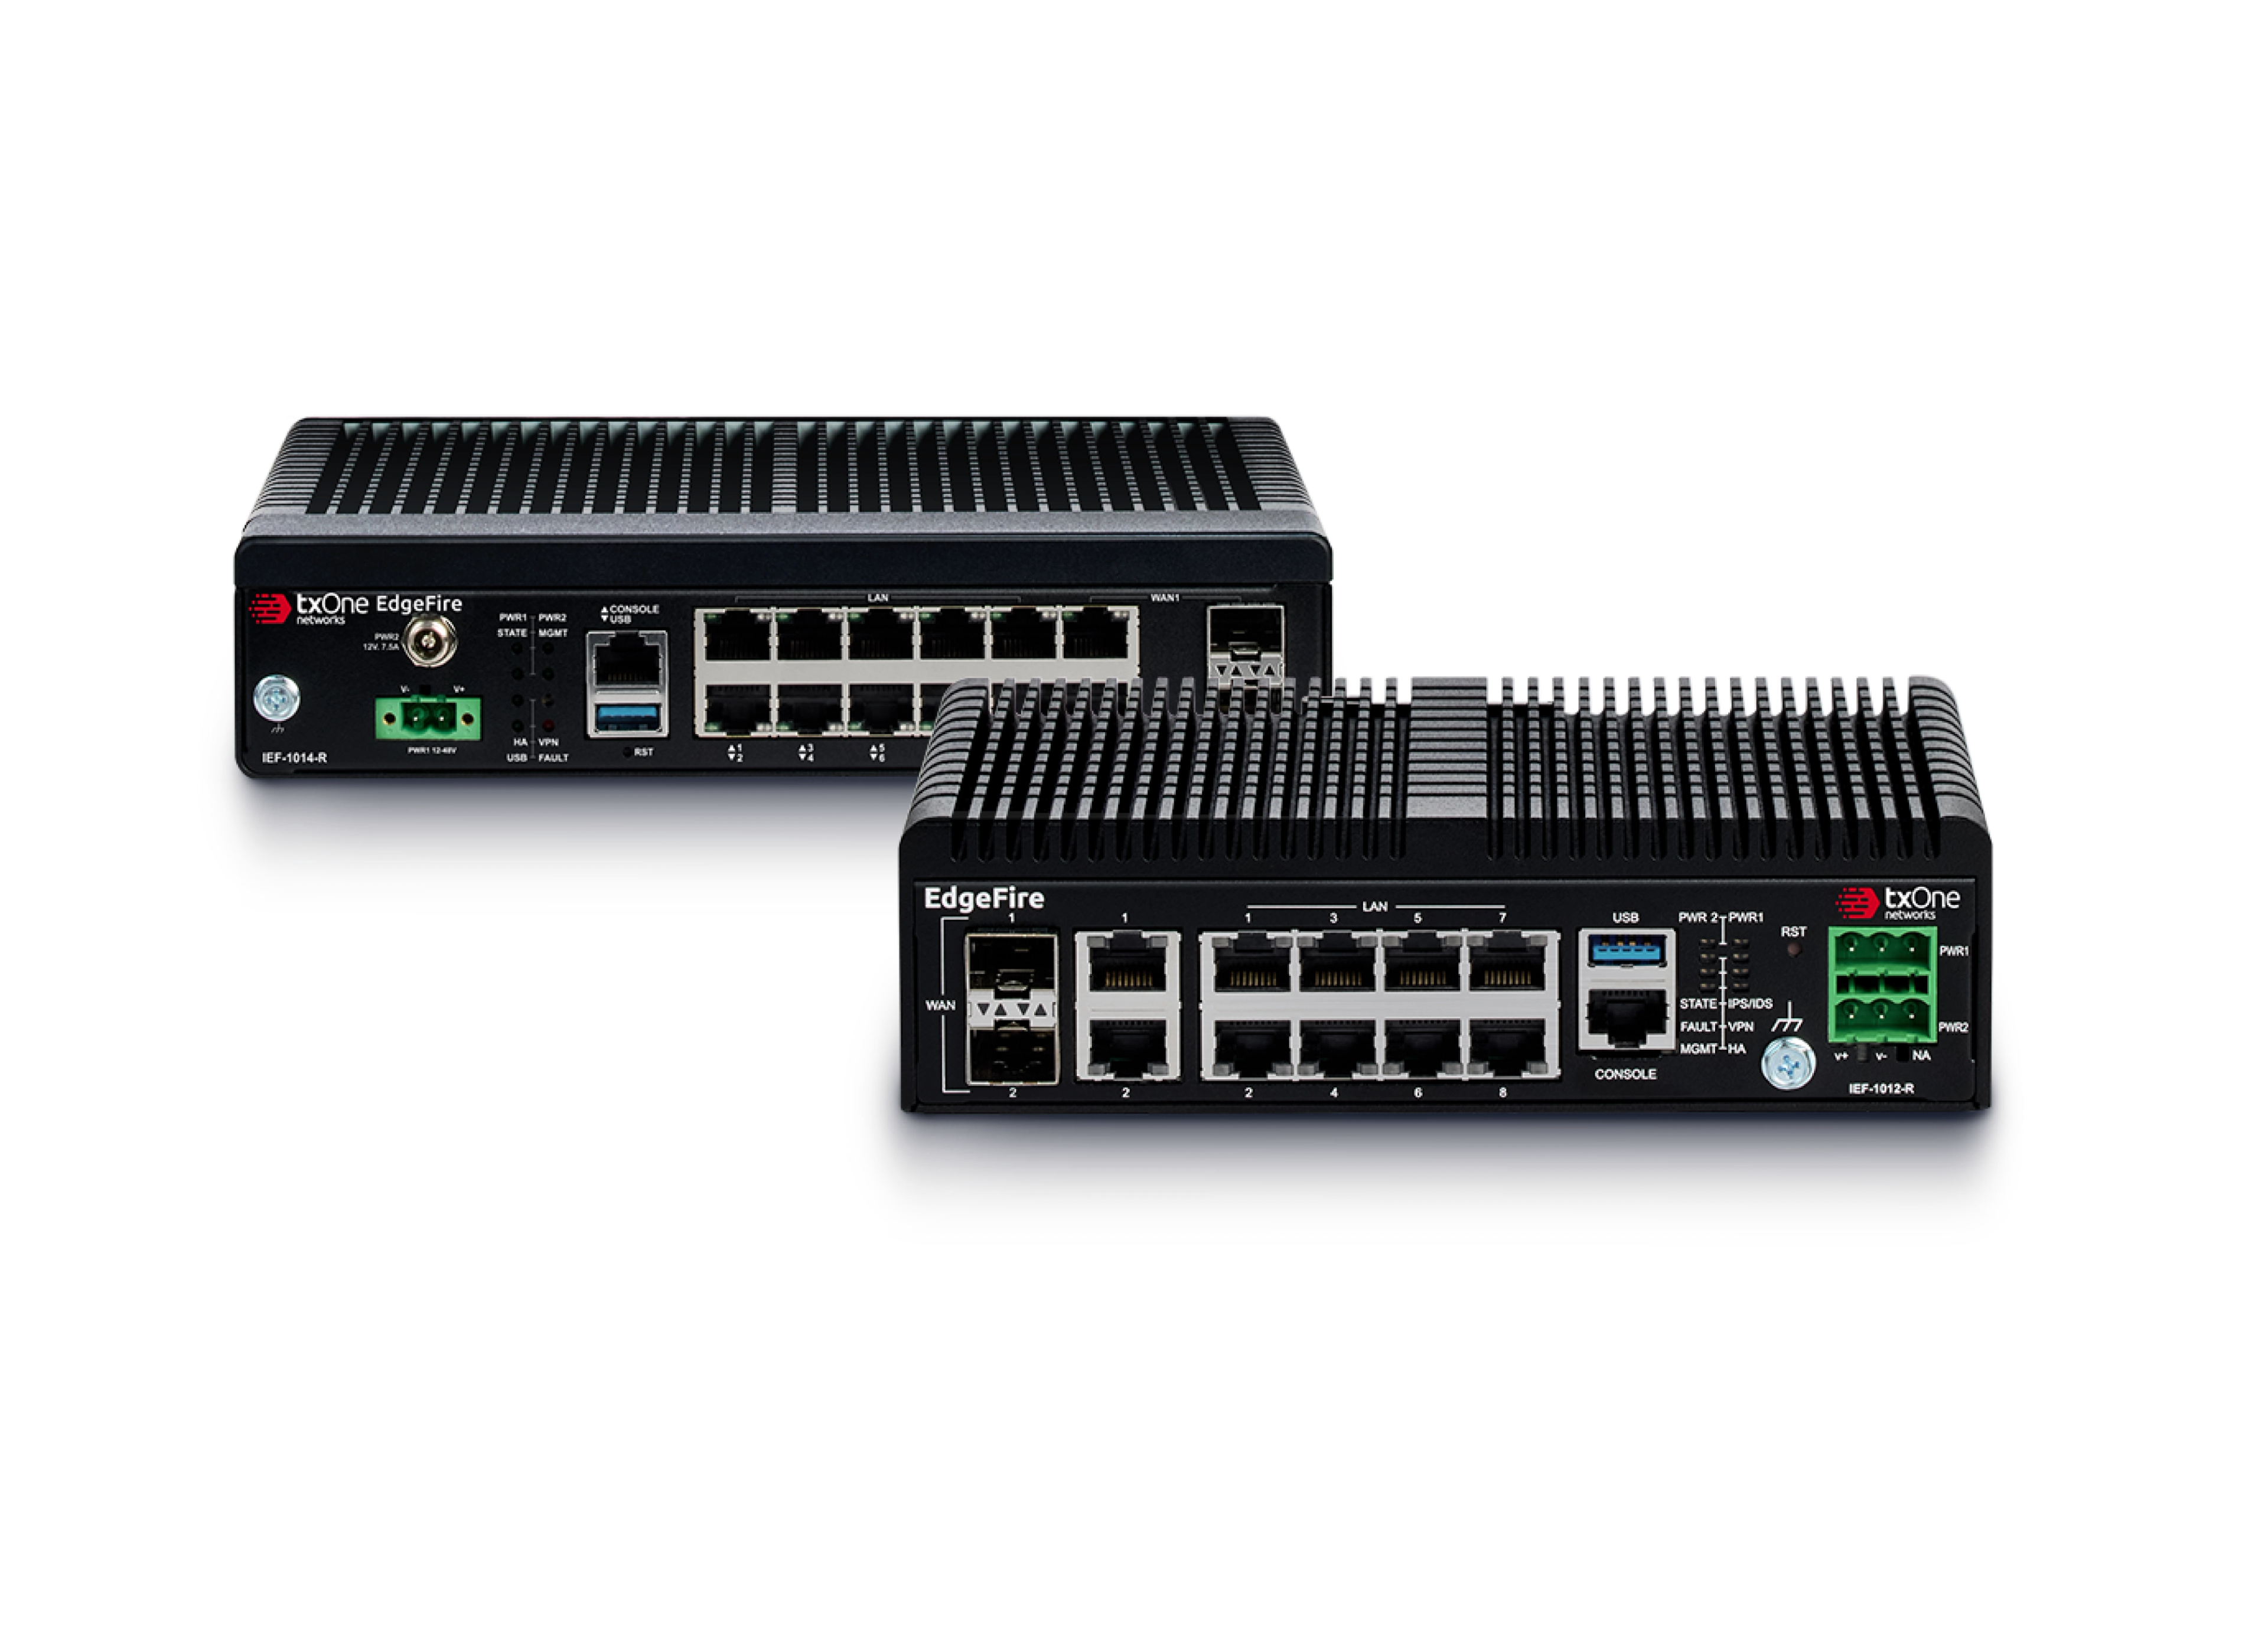
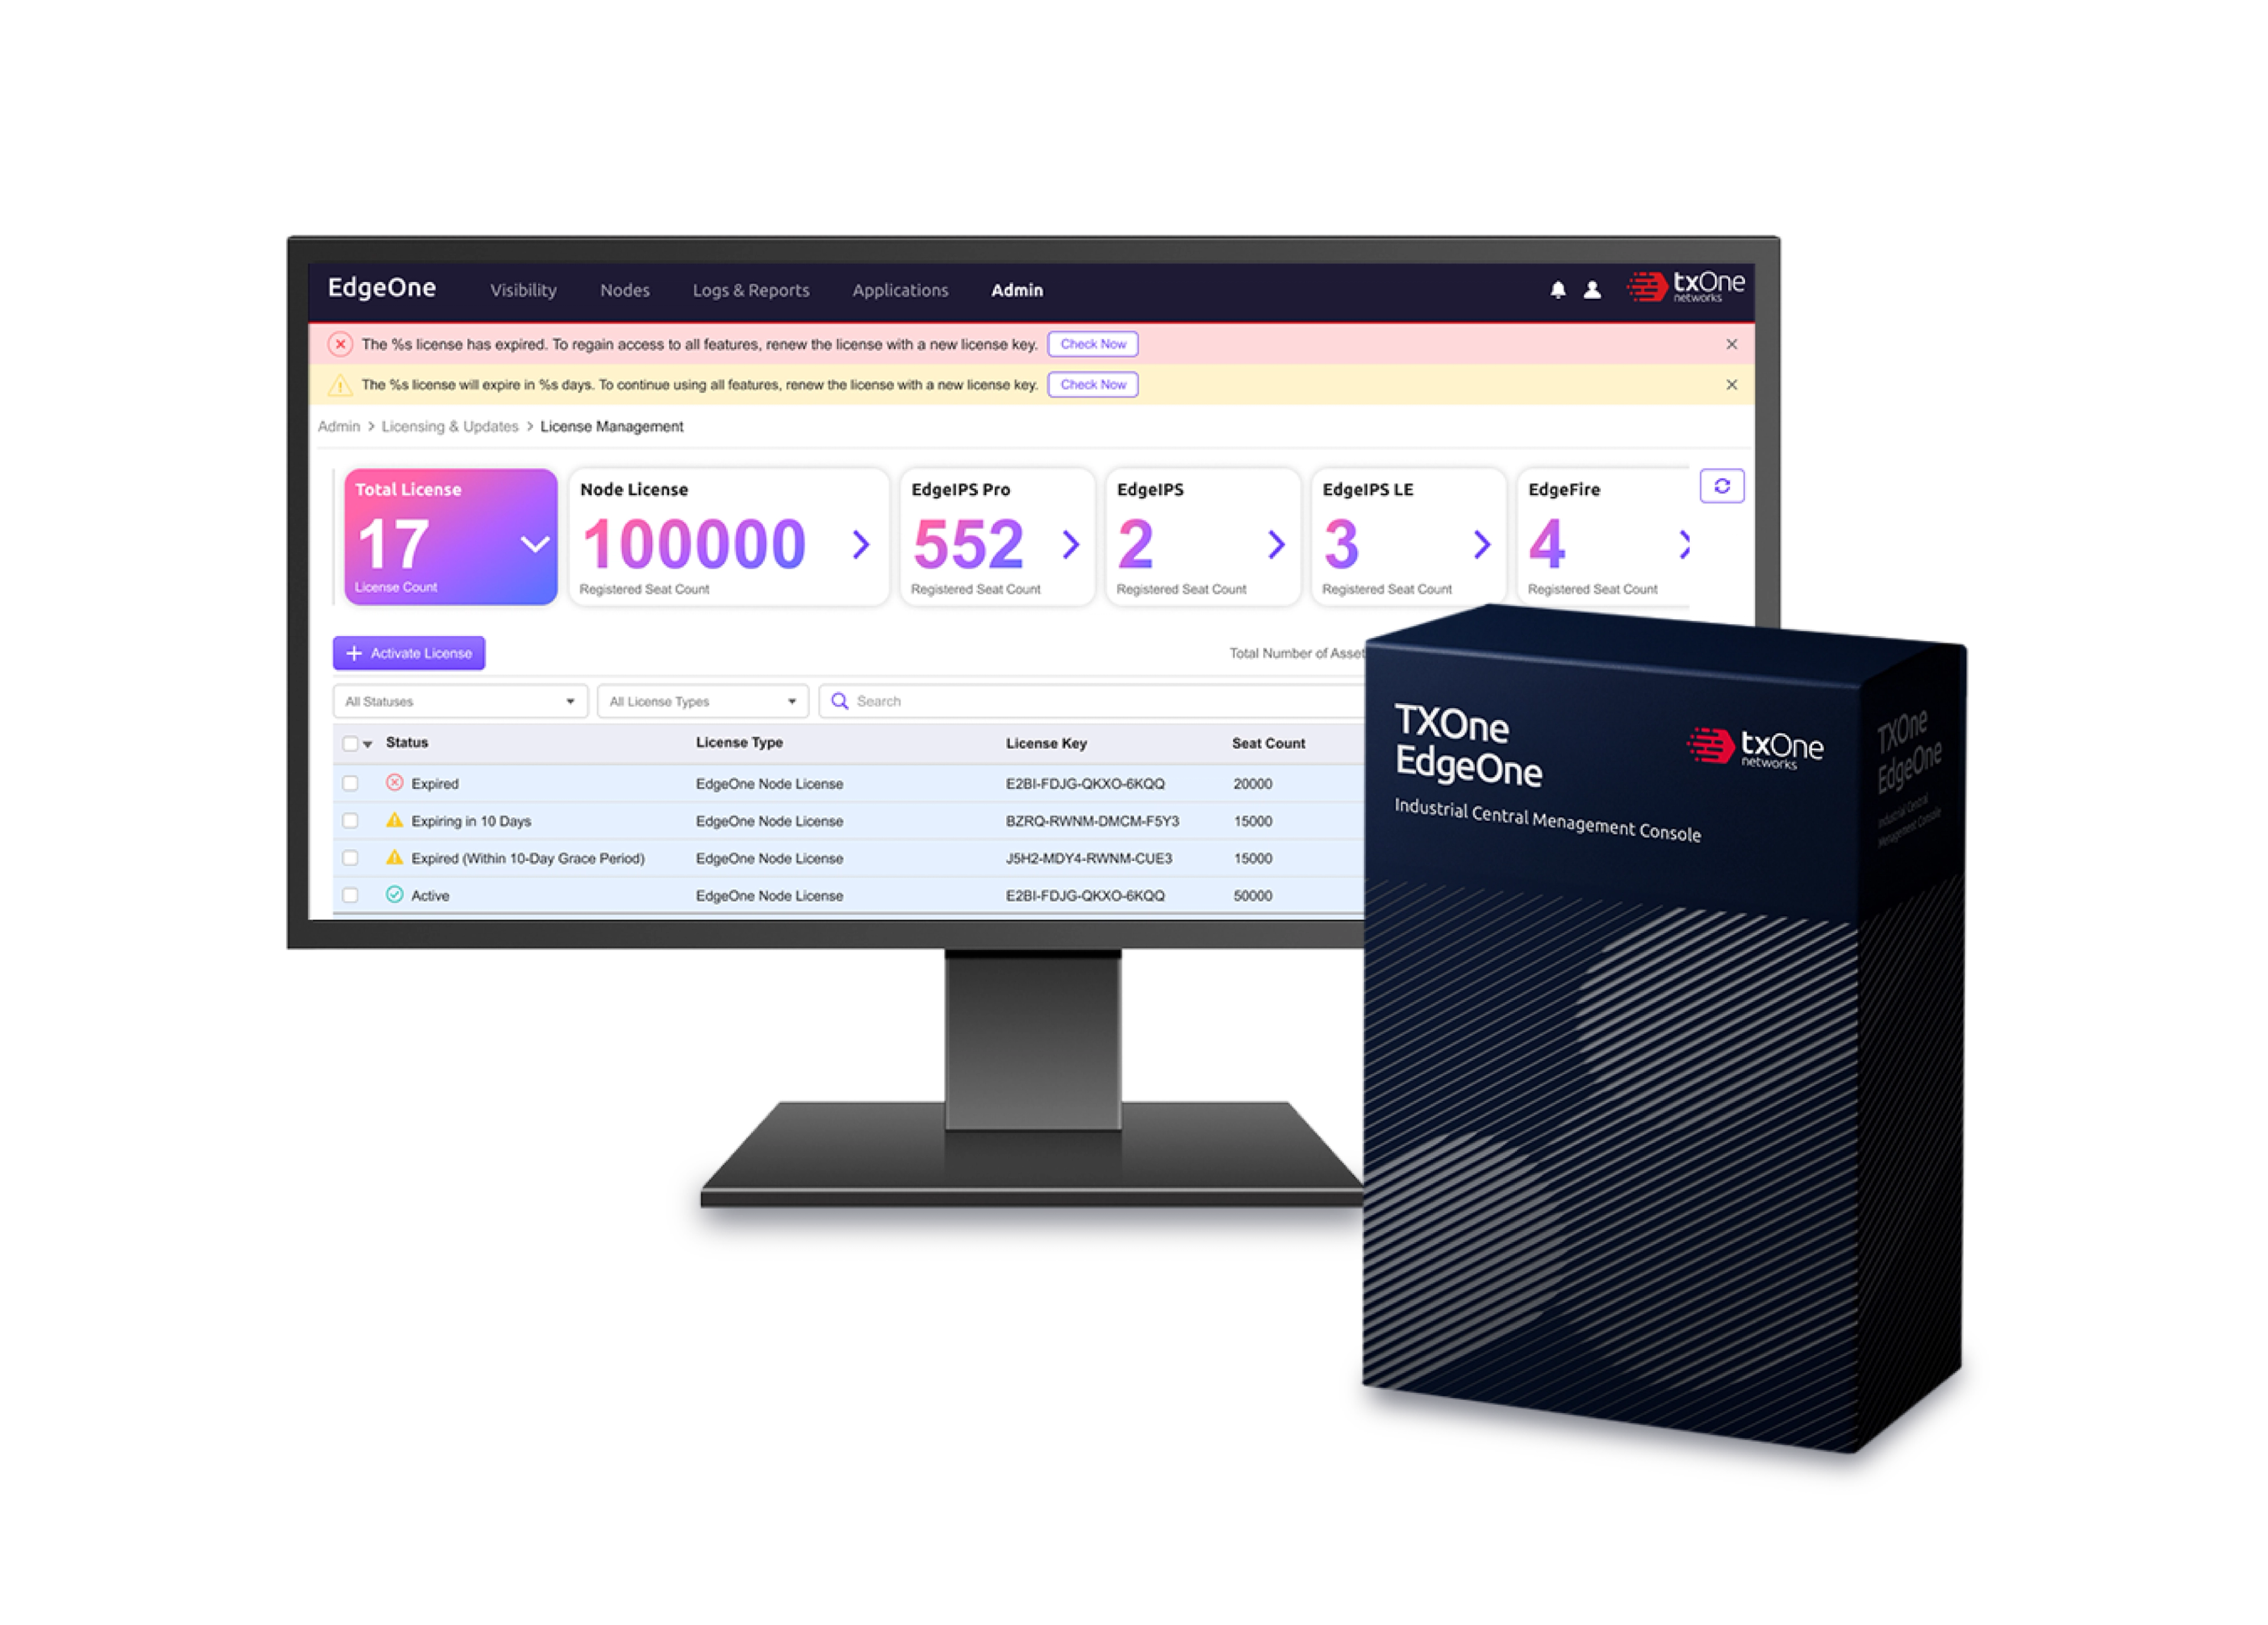
EdgeIPS Family
Intent-Based Industrial IPS
Scalable OT network security with predictive detection and intelligent policy automation
OT network security with AI-driven, asset-centric auto rule learning and policy generation, plus CPSDR predictive security across 180+ industrial protocols. Fail-safe bypass keeps your network running if a device fails. Choose from single-segment units, multi-segment models, rack-mount systems, or a virtual appliance. The family scales to 48 segments in one device and up to 40 Gbps threat prevention throughput.
- Up to 40 Gbps threat prevention throughput
- Fail-safe bypass on every hardware model keeps your network running
- AI-powered policy in hours, not weeks, with 90%+ less manual rule-writing
- Physical or virtual appliances, the same protection either way
- 100,000 policy rules per device for granular control
- CPSDR-powered OT protocol intelligence
Technical Specifications
Security Features
Operation Modes
Certifications
Model Performance (212F)
Model Performance (4016F)
Model Performance (2096)
Model Performance (vEdgeIPS Pro)
What Our Customers Say
“Within this context, TXOne Networks emerged as the ideal technology partner, capable of responding precisely to Ansaldo Energia’s requirements.”
“Thanks to OT security solution Stellar, TXOne Networks helps us mitigate risks that we couldn't address yesterday without making significant financial investments.”
Network Security Resources
Explore technical documentation, case studies, and best practices for OT network security
Technology as a Strategic Ally in Protecting Production Environments
Energy production environments such as power generation plants operate highly interconnected industrial control systems that must remain continuously available. As digital transformation and remote maintenance increased connectivity across IT and OT domains, Ansaldo Energia faced growing exposure to cyber threats targeting legacy assets, engineering workstations, and critical production networks. The organization required… Read more
EdgeIPS Pro 2016F/4016F Datasheet
EdgeIPS Pro 2016F and 4016F are rack-mounted intrusion prevention systems purpose-built for large industrial facilities running fiber infrastructure, delivering 20 to 40 Gbps threat prevention throughput without becoming a bottleneck in the network they protect.
Beyond Replacement: Securing What Can’t Be Replaced Through Strategic Life Extension
Executive Summary Industrial organizations face a critical decision point with their legacy operational technology: accept growing cyber risks, isolate critical systems from needed connectivity, force expensive premature replacement, or pursue strategic asset life extension. Recent industry data reveal that 85% of organizations struggle with the security limitations of legacy systems, while forced replacement strategies cost… Read more
See All Resources
Browse all resources related to network security
Secure Your Industrial Networks Today
Protect your critical OT networks with inline prevention that blocks threats in sub-seconds, deploys in 60 minutes, and provides operational continuity assurance through bypass technology.