
You Can't Patch PHP You Didn't Install: What PHP2Shell Means for OT
PHP2Shell hits PHP inside OT devices only vendors can patch. Here's how to reduce exposure before firmware arrives.
11/5/2026
Stay current on emerging vulnerabilities, advisories, and the evolving threat landscape as our technical writers and threat research team cover sector-specific impacts, organizational responses, and regulatory developments
PHP2Shell hits PHP inside OT devices only vendors can patch. Here's how to reduce exposure before firmware arrives.
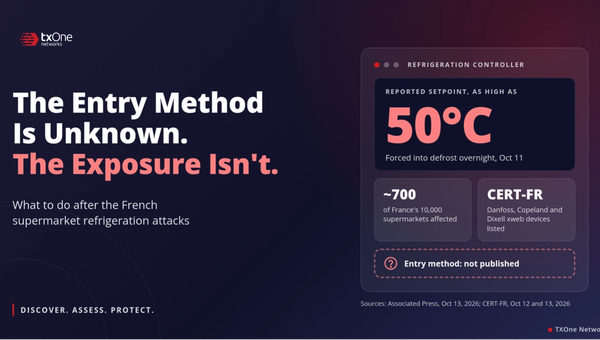
The entry method behind the French fridge attacks is unknown. Here's how to close the exposure now.

Part 1 of the Discover. Assess. Protect. series
Part 2 of the Discover. Assess. Protect. series
Part 3 of the Discover. Assess. Protect. series

ISA/IEC 62443 is the global benchmark for securing industrial automation and control systems. Here are its core protection principles, the three challenges that stall adoption, and how TXOne helps you comply.
The IT/OT convergence is a critical step in enhancing operational efficiency, and TXOne Networks empowers organizations to navigate this transition with confidence.
The NERC Critical Infrastructure Protection (CIP), currently in its fifth iteration, is a mandatory standard that covers access control, personnel safety, physical security, network security incident response, and disaster recovery for large-scale power systems.
What is OT? Operational Technology (OT) cybersecurity is key to protecting factories, power grids, and water systems from cyber threats. While IT focuses on data, OT cybersecurity ensures that the physical processes behind critical infrastructure, manufacturing, energy, and utilities are safe and reliable. This guide looks at what makes OT security unique. It explains why… Read more
TXOne Threat Intelligence System honeypot data for January–June 2026 shows attackers leaning hard on old exposure rather than novel exploits. Three independent telemetry streams — CVE-tagged IPS hits, unique payload diversity, and ICS/OT protocol scanning — all spiked in March, though raw session volume peaked in May.
Air gaps were once the gold standard for protecting OT assets. In the ransomware era, they aren't enough. Wi-Fi and Bluetooth, maintenance staff laptops, and supply chain infections all cross the gap — and air-gapped devices can't update their own scan patterns.
TXOne Networks is IEC 62443-4-1 certified — learn what secure-by-design development means for industrial cybersecurity and why it matters for OT environments.

Modern OT environments, particularly those undergoing digital transformation and IT/OT convergence, have become valuable targets. While many attacks still originate in IT networks, their potential to disrupt operations has elevated the risk profile of OT environments. The following are selected ransomware incidents from Q1 2026 that impacted operations

Your last OT security assessment produced findings. Probably a lot of them. Vulnerability counts, asset inventories, risk scores, maybe a color-coded heat map. The report was delivered. Leadership reviewed it. The security team was asked to build a remediation plan.

A vulnerability rated 9.8 on an HMI controlling a validated production line is not the same as a 9.8 on a development workstation. The CVSS score is identical. The operational risk is not.

The first site is easy. You deploy OT security tools, configure policies, run an assessment, and produce a report. The team manages it directly. It works.

In October 2025, Microsoft ended its support for Windows 10, adding yet another unsupported platform to the list that OT environments quietly continue to run. A familiar problem getting harder to ignore, adding to the dilemma we covered last year.
Recent advisories and reporting have highlighted cyber activity targeting internet-facing Operational Technology devices, particularly Rockwell Automation and Allen-Bradley PLCs such as CompatLogix and Micro850 models. While media coverage tends to focus on who may be behind these campaigns, the more important question for industrial organizations is: why are these… Read more

When geopolitical tensions rise, critical infrastructure becomes an obvious target. As key nodes in global trade, ports handle the flow of goods that economies depend on. A successful cyberattack does not just disrupt operations at a single facility; it can delay imports and exports across interconnected supply chains, trigger economic losses, and erode the… Read more
By: Austen Byers, Technical Director, TXOne Networks
The real problem isn’t what you can see. It’s what you can’t stop.
A critical authentication bypass (CVE-2026-24061) enables unauthenticated root access on GNU inetutils telnetd. Three attack waves began January 22, 2026, progressing from reconnaissance to active weaponization.
By: Chizuru Toyama, TXOne Threat Research
The Health Level 7 (HL7) communication protocol was created to effectively and rapidly share Electronic Health Information (EHI). This standard has been widely used in the medical industry for decades, undergoing continuous development which has produced multiple transmission formats. While HL7 enables efficient medical information sharing, its reliance on outdated communication formats has incurred… Read more
Author: Chizuru Toyama, TXOne Threat Research
International aviation relies on systems built for reliability in closed networks, not for threat resistance in interconnected environments.

Here’s a scenario you might find upsettingly familiar: you’ve got a workstation that’s been functioning reliably for years, managing a critical production line. The system runs custom software that talks to controllers through industrial protocols, and everyone knows not to touch it.
Author: Chizuru Toyama, TXOne Threat Research
The implications of a supply chain cyberattack can be widespread and devastating for the victimized company.
The 2025 SANS ICS/OT Cybersecurity Budget Report highlights a troubling reality: USB devices and contractor laptops remain among the leading causes of industrial security incidents. Despite years of awareness, investment still lags behind the risk. This article explores why the gap persists and what it means for organizations today.

Responsible for everything from potable water to wastewater sanitation, the Water and Wastewater Systems (WWS) sector operates behind the scenes to uphold the function of our modern society.
Author: Chizuru Toyama, TXOne Threat Research
Author: Chizuru Toyama, TXOne Threat Research
If you run industrial operations, you’ve probably felt it: the flood of alerts that don’t specify what’s urgent, the risk of downtime if you touch fragile systems, and the growing pressure to demonstrate compliance.
CVE-2025-32433 is a critical unauthenticated remote code execution (RCE) vulnerability in the Erlang/OTP SSH daemon.
When a cyberattack hits any sector of critical infrastructure, it can directly impact the public by disrupting people’s lives. But when it comes to public transit, the stakes are even higher.
UNC3886 is a state-sponsored advanced persistent threat (APT) group first identified by Mandiant in 2022. Believed to be linked to China, UNC3886 has been active since at least 2021.
From the moment it emerged, ransomware has been a thorn in the side of organizations. But with the rise of ransomware-as-a-service and the growing convergence between IT and OT, that thorn has evolved into something far more dangerous—sharper, faster, and backed by a thriving criminal business model. Now that governments are moving to ban… Read more
Rail systems are built to keep moving safely, predictably, and without interruption. That’s exactly what makes them so vulnerable.

Since 2024, the number of ransomware attacks targeting the food and agriculture sector has been increasing. Some gangs are focusing on OT environments in particular, which makes ransomware a major threat that cannot be ignored.
In April 2025, the National Security Agency (NSA) released their report, Operational Technology Assurance Partnership (OTAP): Smart Controller Security within National Security Systems, to address the lack of formal testing and conformance standards for smart controllers. These are embedded devices in OT environments that automate physical processes and connect to networks.

In the race toward digital transformation, one persistent challenge continues to jeopardize progress—legacy systems in OT environments.
Author: Chizuru Toyama, TXOne Research
Supply chains have always carried an unavoidable level of unease. Volt Typhoon more than justifies that unease.
The Cyber Resilience Act (CRA) entered into force on 10 December 2024. While its main tenets will not apply until 11 December 2027, the reporting requirements will take effect earlier, starting on 11 September 2026.
RansomHub operates like a well-oiled machine, recruiting affiliates (the cybercriminals that do the dirty work of launching attacks) and providing them with their ransomware payloads for both Linux and Windows endpoints. Their true innovation, however, lies in their multi-level access intended to attract various levels of cybercriminals, ranging from low-skilled newer entrants to the scene… Read more
Cyberattacks on the food and beverage (F&B) manufacturing sector have surged, mirroring trends seen across industrial control systems (ICS) and critical infrastructure.
Virtual patching is a vulnerability-shielding tactic that protects assets by implementing layers of security policies and rules. These layered security measures prevent and intercept an exploit from taking network paths to and from a vulnerability.
TXOne’s prevention-first approach to industrial cybersecurity receives validation in the first-ever Gartner evaluation of CPS security platforms. We are proud to announce that TXOne Networks has been recognized in the inaugural Gartner Magic Quadrant for Cyber-Physical Systems Protection Platforms, 2025.
Author: Ta-Lun Yen, TXOne Research
In our previous episode, we covered a series of attacks that bypass firewall/routing rules on multiple SSL VPNs. In this article, we will dive deeper into the vulnerability details and explore how SSL VPN works in general.
The automotive industry is undergoing a rapid digital transformation driven by the integration of advanced technologies.
Innovation in new drugs, treatments, and therapies is crucial. Consequently, research and development (R&D) data has become a high-value target for cybercriminals. The most representative example is the rollout of COVID-19 vaccines and other breakthroughs in life sciences, which significantly increased the risks of cyberattack faced by the pharmaceutical industry.
Since 2015, ransomware attacks have become a significant threat that organizations and enterprises cannot afford to ignore, especially as critical infrastructure sectors (CI) increasingly embrace digitalization.
Companies in the food industry are seen as some of the most vulnerable potential victims of cyberattacks. This is due to a combination of legacy systems and modern technology being used throughout the supply chain, along with an absence of robust, industry-wide cybersecurity practices. In many cases, investment into cybersecurity measures is hard to justify… Read more
Since September 2020, there have been several global supply chain attacks such as SolarWinds, Kaseya, NPM IconBurst, and Cyber Av3ngers Unitronics. Many of these incidents involved nation-state actors and resulted in significant disruptions and failures.
Automation technologies are widely used in critical infrastructures to ensure continuous operation. Beyond productivity, cost, and accuracy, risk reduction is also a significant benefit.
Modern healthcare institutions use digital technology to manage patient information, nursing services, medical testing, and even assist in medical surgeries. It is now common for medical staff to rely on IT and OT systems.
Cybersecurity in the food supply chain has become a major concern amid increasing attacks on companies like Dole, Mondelez, and Sysco. The food industry is one of the most important in the world, with any supply chain disruptions causing widespread harm, panic, and concerns about public safety. This risk has only increased with more technology… Read more
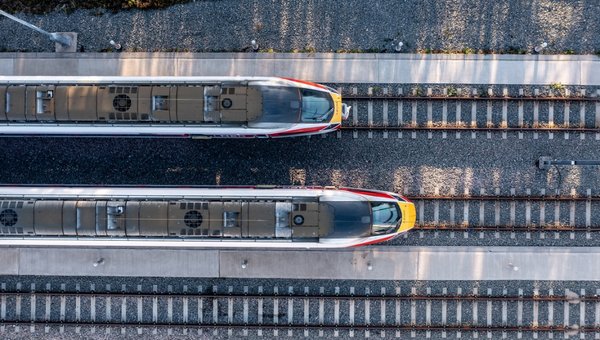
It’s not an unusual plotline for Hollywood movies—our intrepid protagonists need to stop and hijack a train carrying high-value national organization or military assets and the audience is treated to an action scene of them carrying this out.
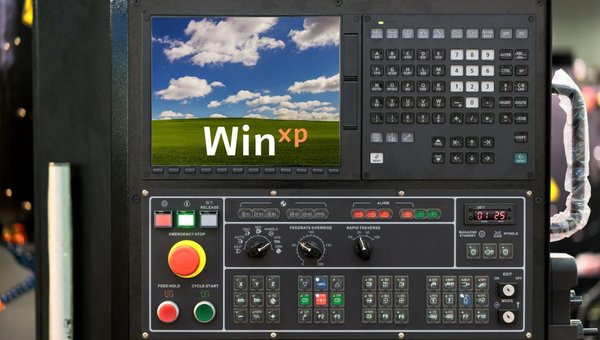
Within Operational Technology (OT) environments, legacy Windows systems remain a critical part of the infrastructure, presenting unique security challenges. For the purposes of this article, legacy Windows systems refer to those systems no longer receiving updates, patches, or direct support from the developer during their product lifecycle.
The food and agriculture industry faced over 160 cyberattacks in 2023, causing supply chain disruptions worldwide. The food manufacturing industry is the seventh most attacked globally.
Semiconductors are an indispensable part of modern electronic products and are also a fundamental basis for the development of the AI industry.
Introduction According to recent cybersecurity media reports, a new destructive ICS malware named Fuxnet has been discovered. This incident is allegedly linked to the Blackjack hacker group, which is associated with Ukrainian security agencies. It involved a major attack on Moscollector, a Moscow-based company responsible for managing critical infrastructure such as water supply, sewage treatment,… Read more
In recent years, the frequency and success of exploits targeting firewall vulnerabilities have been alarmingly high. A notable incident in 2024 involved the disclosure of five consecutive zero-day vulnerabilities in Ivanti Connect Secure, with some vulnerabilities being actively exploited to enable unauthorized remote code execution on affected devices, and even weaponized by nation-state actors.… Read more
On June 29, 2023, the European Parliament and the Council of the European Union announced Regulation (EU) 2023/1230, which will replace the existing Machinery Directive 2006/42/EC. This updated regulation revises the product scope and conformity assessment procedures originally covered by Directive 2006/42/EC.
HMIs (Human Machine Interfaces) can be broadly defined as just about anything that allows humans to interface with their machines, and so are found throughout the technical world.
In today’s OT threat environment, PLCs (Programmable Logic Controller) have become one more attack surface for threat actors looking for easy entry points to industrial facilities.
The automotive industry has long attracted cyber threat groups due to its expansive reach, encompassing vehicle manufacturing technologies and critical operational infrastructures.
SSL VPN (Secure Sockets Layer Virtual Private Network) is an essential technology for enterprises, allowing users to securely connect to internal networks over insecure networks such as the internet. This is crucial for maintaining cybersecurity as it enables employees to work from home or remotely.
Cybolt is a “pure-play” cybersecurity firm and a TXOne Certified Partner that provides a broad range of cybersecurity services to clients throughout the Americas and is now expanding into European markets. Cybolt’s purpose is to “Identify, prevent, and neutralize risks to create spaces of trust.” “We provide managed security services as well as deskside services… Read more
In 2023, the cybersecurity challenges in the Operational Technology (OT) and Industrial Control Systems (ICS) landscape reached unprecedented levels.
This article was originally published on SDM Magazine on Feb 28, 2024, written by Dr. Terence Liu, CEO of TXOne Networks.
This article was originally published on Manufacturing.net on Feb 29, 2024, written by Dr. Terence Liu, CEO of TXOne Networks.
Kutoa is a newly formed company whose purpose is to help clients with cyber-physical environments “build cybersecurity capacity”, as explained by Dave Cullen, one of their four founding partners. “Our approach is that we don’t have only ‘an OT environment to secure’, but rather, ‘a connected organization to serve.’” While they officially launched in January… Read more
The semiconductor industry, pivotal to technological advancement in the current digital transformation era, cannot afford to overlook its cybersecurity. To address this, SEMI has introduced two key standards: SEMI E187 and E188.
Jacob Marzloff is the co-founder and president of Armexa, an OT/ICS cybersecurity firm based in Houston, Texas, and a TXOne Certified Partner. Jacob grew up in southern Louisiana, where the oil, gas, and chemical industries are part of the landscape. He spent a lot of time around the plants, working different jobs and gathering irreplaceable… Read more
Automakers like Tesla, Renault, Ford, and Nissan use digital twins to speed up design, predict maintenance, and improve production. But a virtual copy of a physical system also gives attackers a new way in. This guide covers five key threats to digital twins, from reconnaissance to model corruption, and how to defend against them.
An OT risk assessment shows you how much cyber risk your organization carries and what to fix first. This handbook covers the five main benefits, from risk prioritization to compliance and cost savings. It also gives a step-by-step way to measure impact and apply OT zero trust to protect critical infrastructure.